
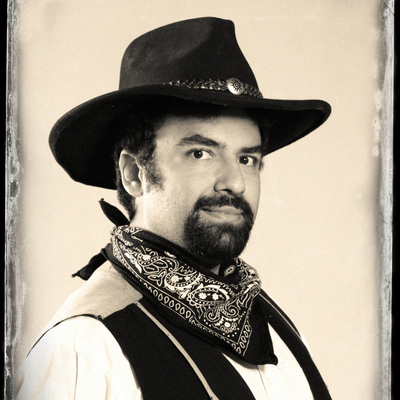
Mohammad-Ali A'râbi
Docker Captain, Author of "Docker and Kubernetes Security", Senior Software Engineer @ JobRad
Freiburg, Germany
Actions
Mohammad-Ali A'râbi is a Senior Backend Engineer at JobRad GmbH, Docker Captain 🐳, and Snyk Ambassador 🛡️ with over 20 years of coding experience and a deep passion for DevSecOps and container security.
He is the author of "Docker and Kubernetes Security", a hands-on guide to securing containerized environments from build to runtime. As a community leader, Mohammad-Ali founded the Docker Meetup in Freiburg (now Cloud Native Freiburg), organizing dozens of events that connect developers across the Black Forest region.
Beyond his book, he shares advanced Git and Docker insights through his Git Weekly newsletter and frequent conference talks. When he's not securing supply chains or hosting meetups, you'll probably find him building side projects, collecting superhero figures, or playing Mortal Kombat. 🎮
Badges

Area of Expertise
Topics
Workshop: Java Supply Chain Security with Docker
Secure your Java containers from build to deployment in this 2-hour hands-on workshop!
Join Docker Captain Mohammad-Ali A'râbi for a practical deep dive into Java supply chain security using Docker's latest tools. You'll learn how to containerize Java apps securely, automate builds, generate SBOMs, and verify them through attestations.
Key Topics:
- 🐋 Docker Init: Containerize Java applications quickly and consistently
- 🚀 Docker Bake: Automate and optimize multi-stage builds
- 📜 Docker SBOM: Generate detailed Software Bills of Materials for Java containers
- 🧾 SBOM Attestations: Sign and verify build artifacts to secure your supply chain
- 🔍 Docker Scout: Scan for vulnerabilities and ensure image integrity
Perfect for Java developers, DevOps engineers, and security practitioners who want to understand and apply modern supply chain security practices using Docker’s newest features.
Dockerize Java Securely: SBOMs + Attestations + Bake
Containerizing Java applications is easy. Containerizing them securely is not.
In this session, we'll explore how to strengthen your Java Docker builds with Software Bill of Materials (SBOMs) and registry attestations. Instead of generating a single SBOM at the end, you'll see how to extract SBOMs at every stage of a multi-stage build, catching vulnerabilities that would otherwise slip through.
We'll cover:
- Why SBOMs are critical for modern Java applications
- How to integrate SBOM generation directly into Docker builds
- Use Docker Bake to make it delicious
- Pushing SBOMs as attestations to your registry for supply-chain visibility
- Use hardened images to make it easier
- Asking Johnny Cage to sign the images and their SBOM attestations
Live demo: Containerizing a Spring Boot app with security built in
Beyond SBOMs: The Future of Container Supply Chain Security
When a single phished NPM maintainer led to 18 compromised libraries—including Chalk and Debug, downloaded billions of times weekly—it proved one thing: SBOMs alone aren't enough.
In this talk, Docker Captain Mohammad-Ali A'râbi explores how modern supply-chain attacks unfold and how the next generation of tools can prevent a repeat of the September 2025 NPM breach.
What you'll learn:
- 🧠 Understand how the 2025 NPM supply-chain attack happened—and why traditional SBOMs couldn't stop it.
- 📦 Pin & lock dependencies to prevent malicious updates from sneaking in.
- 🧱 Generate, sign, and verify attestations using Docker Scout + Cosign + Rekor.
- 🔒 Adopt zero-trust build pipelines with SLSA levels + OCI 1.1 referrers.
- 🧰 Defend proactively with seven practical strategies: block lifecycle scripts, use hardware keys, and continuously scan with Snyk / Trivy / Scout.
- 🚀 Turn compliance into confidence by making your entire container lifecycle verifiable.
BaselOne 2026 Sessionize Event
WeAreDevelopers World Congress 2026 - Europe Sessionize Event
DevOpsDays Zurich 2026 Sessionize Event
JCON EUROPE 2026 Sessionize Event
Jfokus 2026 Sessionize Event
WeAreDevelopers World Congress 2025 Sessionize Event
PlatformCon 2025 Sessionize Event
DevFest Nuremberg 2024 Sessionize Event
90DaysOfDevOps - 2024 Community Edition Sessionize Event
WeAreDevelopers Live 2023 (Season 6) Sessionize Event
Appdevcon / Endpointcon 2023 Sessionize Event
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top