
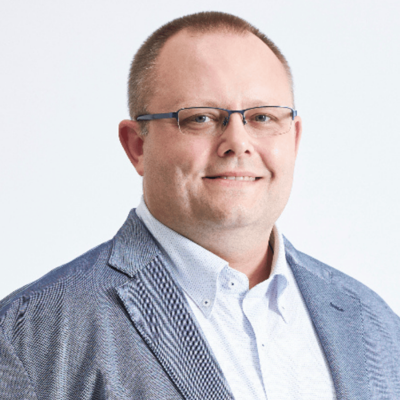
Charles Green
Systems, not guesswork. | Lean. Fast. Secure AI.
Actions
Charles Green is the founder of Lean Security, a community-driven resource for modern security teams building in fast-moving environments. With over two decades of experience across the U.S. and Japan, including roles as a two-time CISO, Charles has led red teams, blue teams, and cloud security programs in fintech and SaaS.
Today, his work centers on AI-driven security, helping teams automate threat modeling and scale security using intelligent pipelines. Through frameworks like the Find–Fix–Flow feedback loop and tools like the Lean Security Canvas, he enables teams to identify real-world risks directly from architecture diagrams, cloud metadata, and source code without slowing down delivery.
Based in Japan for over 18 years, Charles is an active contributor to the global security and fintech communities. He regularly shares lessons, frameworks, and tools through Lean Security and has recently spoken at Bsides on securing multi-agent AI systems.
Links
Threat Modeling with Multi-Agent AI: Beyond the Basics
Threat modeling is broken. Confident engineers provide incomplete information, documentation is outdated, and critical vulnerabilities slip through the cracks.
This session unveils a revolutionary approach: multi-agent AI systems that dynamically extract and analyze real-time infrastructure data, automatically mapping complex technology landscapes to potential security risks.
By leveraging AI agents specialized in cloud metadata extraction, architectural analysis, and risk correlation, we transform threat modeling from a static, error-prone process into a live, intelligent vulnerability discovery mechanism.
Attendees will see how these autonomous agents:
- Uncover hidden inconsistencies in system architectures
- Generate testable security insights
- Reduce human bias and tribal knowledge limitations
- Provide actionable, context-aware threat assessments
Dive into the future of cybersecurity, where AI doesn't just assist, it leads the threat detection revolution.
AI Agents: Your Automated Hacking Apprentice
Penetration testing is time-consuming and skill-intensive. What if AI could automate the grunt work? Our research reveals how AI agents can transform offensive security, making advanced reconnaissance accessible to everyone.
Imagine sending an AI agent to:
- Automatically map network vulnerabilities
- Generate initial exploit strategies
- Perform intelligent port scanning
- Correlate publicly available threat intelligence
- Create preliminary attack path recommendations
These AI agents aren't replacing skilled professionals. They're your new reconnaissance sidekick, handling repetitive tasks and surfacing interesting attack surfaces faster than manual methods.
We'll demonstrate live how AI agents can:
- Reduce manual reconnaissance time
- Highlight unexpected network weaknesses
- Provide actionable initial insights
- Lower the entry barrier for security testing
Perfect for security professionals, developers, and anyone curious about the next frontier of automated security testing.
BSides Tokyo 2025
Threat Modeling with Multi-Agent AI
Threat modeling is essential, but it’s often slow, frustrating, and incomplete. Documentation is outdated, architecture diagrams are missing, and worst of all, confident and helpful engineers give you the wrong information.
This talk explores how multi-agent AI systems can automate core parts of the threat modeling process by extracting live data from cloud metadata, architecture diagrams, and documentation, then mapping it to STRIDE risks. These agents work together to uncover inconsistencies, reduce guesswork, and generate testable outputs for security teams.
Rather than relying on static templates or tribal knowledge, this approach builds a live, accurate view of your system. You’ll leave with practical ideas to make threat modeling faster, more reliable, and easier to scale.
Charles Green
Systems, not guesswork. | Lean. Fast. Secure AI.
Links
Actions
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top