
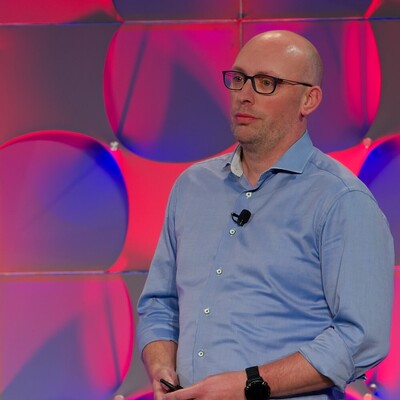
Danny de Haan
Database Security & Infrastructure Advocate
Roermond, The Netherlands
Actions
Danny is a seasoned IT professional with nearly 20 years of experience, specializing in SQL Server and the Microsoft Data Platform. With over 15 years dedicated to SQL Server, he's built a reputation for his expertise in Security, Risk Management, and Compliance, ensuring that industry best practices and regulatory requirements are met from an infrastructural perspective.
He's a passionate advocate for secure database usage, regularly speaking at conferences and events where he shares insights on (data) security and compliance.
Area of Expertise
Topics
Securing the SQL Server Data Platform: Preventing Data Loss and Ensuring Data Privacy
In today’s world of escalating cyber threats, securing your SQL Server environment has become a critical priority. The phrase "It's not a matter of if, but when you're going to be hacked" has never been more true. With external attacks becoming more sophisticated, organizations must prepare for the inevitable and safeguard their SQL Server data platform against data breaches, unauthorized access, and data loss.
This talk will focus on the essential steps to secure SQL Server environments against external threats and prevent the loss of critical data. We'll explore how to design a security strategy that reduces the attack surface and ensures your data is protected - even when facing advanced, targeted attacks.
From securing network connections and enforcing strong authentication mechanisms to implementing encryption, we'll discuss a range of practical, actionable measures that will help you safeguard your SQL Server Platform from malicious external actors.
Securing the SQL Server Data Platform: Defining a security strategy
In today’s world of escalating cyber threats, securing your SQL Server environment has become a critical priority. The phrase "It's not a matter of if, but when you're going to be hacked" has never been more true. With external attacks becoming more sophisticated, organizations must prepare for the inevitable and safeguard their SQL Server data platform against data breaches, unauthorized access, and data loss.
This talk will focus on the essential steps to secure SQL Server environments against external threats and prevent the loss of critical data. We'll explore how to design a security strategy that reduces the attack surface and ensures your data is protected - even when facing advanced, targeted attacks.
From securing network connections and enforcing strong authentication mechanisms to implementing encryption, we'll discuss a range of practical, actionable measures that will help you safeguard your SQL Server Platform from malicious external actors. How to monitor and audit these settings, not only for yourself, but also for compliancy purposes.
Database Development with a Security-First Mentality
In today’s increasingly digital world, ensuring the security of data is paramount. This session, will dive into the essential practices and principles of secure SQL Server database development. Attendees will learn how to adopt a proactive approach to database security from the initial stages of development, incorporating best practices to safeguard sensitive information against unauthorized access, data breaches, and malicious attacks.
The session will explore critical security features within SQL Server, such as encryption, authentication, role-based access control, and auditing. Furthermore, we will address the importance of regular security assessments and continuous monitoring to stay ahead of evolving threats.
By the end of the presentation, developers will have the knowledge and tools to integrate security seamlessly into the database development lifecycle, ensuring their SQL Server databases are resilient and compliant with industry standards and regulations.
Kerberos: A deep dive into delegation & SQL Server
In this session, we will explore the inner workings of Kerberos authentication in Active Directory and its critical role in modern network security, with a special focus on delegation and its application to SQL Server environments.
Kerberos is the gold standard for secure authentication in distributed systems, but its complexities - particularly around delegation - can be challenging to navigate. This talk will break down the key concepts of Kerberos, explaining what it is, how it works, from the login process up to the use of services like SQL Server.
We'll be looking into delegation, the technical aspects of it, how the various delegation types work, including their weaknesses and how this relates to our SQL Data Platform.
Last but not least we'll also take a look at attack scenario's hackers use and what you can do to prevent certain attacks.
Securing the SQL Server Data Platform: Strategy, Hardening, and Real‑World Defense
In a world where data breaches, ransomware, and targeted attacks are no longer hypothetical, securing your SQL Server data platform requires more than a checklist; it demands a strategy.
This full‑day workshop takes you on a practical, end‑to‑end journey through designing, hardening, and defending a secure SQL Server environment, whether on‑premises or hybrid.
We begin by establishing the foundations of security by design: understanding threat models, compliance requirements, and architectural decisions that shape a resilient data platform. From there, we dive deep into real‑world hardening techniques across every layer: network, infrastructure, operating system, and SQL Server itself; showing you how to reduce your attack surface and build a platform that’s secure by default.
As the day progresses, we shift from theory to hands‑on implementation. You’ll learn how to enforce strong authentication, secure network paths, apply encryption effectively, and configure your data platform to withstand modern external threats. We’ll explore monitoring strategies, auditing approaches, and how to maintain ongoing compliance without drowning in alerts or paperwork.
Finally, we tackle one of the most overlooked aspects of database security: the human element. You’ll discover how to guide developers toward secure coding practices, prevent accidental data exposure, and build a culture where security is part of everyday development, not an afterthought.
By the end of the workshop, you’ll walk away with a clear blueprint for securing your SQL Server data platform from design to implementation, along with practical steps you can apply immediately to make your environment a harder target than the one next door.
From Reactive to Resilient: Navigating the Data Security Maturity Journey
Most data breaches don’t start with a clever zero-day. They start with basics that were never in place: no MFA, credentials that haven’t been rotated in years, no alert when millions of records leave the building. The fix isn’t another tool. It’s knowing where you stand and what to do next.
This session introduces a vendor-neutral Data Security Maturity Framework that measures how well you protect your data across four levels, from Reactive to Adaptive. We walk through each level with practical examples, then focus on the six core domains every data platform needs: discovery and classification, protection and encryption, access governance, activity monitoring, secrets and key management, and governance and compliance. You’ll see how the same control translates across platforms like SQL Server and PostgreSQL, why weak dependencies cap your real maturity, and where Zero Trust, AI-driven detection and tokenization fit in.
You’ll leave with a self-assessment to run against your own environment, a way to turn the results into a prioritized gap analysis, and a 90-day plan for moving up one level at a time.
Treating Security as a Data Discipline in Your Organization
Security operations rely on logs, alerts, and event data, yet these sources are rarely managed with the same structure, governance, or planning as other organisational data. When Security and Compliance and your data treatment don’t align, the amount of data gathered can become costly, you start looking for that needle in a haystack when you have to analyse your data, or even worse, do a post-mortem after a breach.
In this session, we’ll explore the gaps that appear when data practices are not applied to security products and telemetry. The absence of well-defined data models, retention policies, and optimised queries leads to operational blind spots and unnecessary cost. Leadership often assumes security tooling automatically manages data quality and structure, but advanced analytics, accurate reporting, and faster investigations all depend on intentional data design.
Practical examples will illustrate how structured approaches improve event analysis: visualising anomalies, determining what data to collect, and designing queries that support both investigations and long-term reporting. Regardless of which security product or platform your organisation uses, defining your security and compliance standards allows your data to better support and strengthen detection, reporting and incident response.
We will show you how basic data principles such as retention strategies, clear schemas, governed access, and efficient queries, can provide you the foundation for reliable, actionable and data-driven security operations across your organisation.
You Are Not Prepared: The SQL Server Audit Trail That Goes Nowhere
SQL Server produces thousands of security-relevant events every day: login failures, permission grants, schema changes, privilege escalations, unusual query patterns. Almost none of it reaches the SOC. Security teams assume database teams have the threat covered. Database teams assume the SOC doesn't need the data. The result is a blind spot positioned directly in front of your most sensitive information, and while nobody's watching the threat meter, the boss is already in the room.
This session pulls you out of the fire. We cover what SQL Server actually produces and what's worth collecting; SQL Server Audit, Extended Events, login telemetry, and Agent history each serve a different purpose. From there: structuring data for fast investigation, forwarding it to Azure Monitor, Sentinel, or any syslog-compatible SIEM, and designing alerts that surface real threats without overwhelming the SOC.
The irony is that WoW raiders obsess over log parsers to optimise every raid... Your security team should be doing exactly the same thing.
Come With Me If You Want to Live - Ransomware-Proofing the Data Platform
Most organisations have a backup strategy. Far fewer have a recovery strategy that actually works after a ransomware attack. The difference matters when Judgment Day arrives and the clock is running.
Modern ransomware operators don't act like opportunists, they act like the T-1000. Patient, methodical, and already inside the perimeter long before they strike. Before encrypting production, they spend days or weeks compromising backup agents, corrupting backup files, stripping recovery credentials, and poisoning replicas. They can't be bargained with and they can't be reasoned with. By the time you see the ransom note, the backups you thought you had are already gone.
This session is built around that threat model and the conviction that there is no fate but what we make. We cover immutable backup architectures (Azure Blob immutability, WORM storage, deletion protection) and credential isolation: ensuring backup systems operate behind an identity boundary that production cannot cross. We look at what the 3-2-1-1 model looks like in a real database environment, how to test recovery under full-compromise conditions, and the process failures that turn survivable attacks into total losses.
The Kill Chain - From Phish to Sysadmin on SQL Server
Most security talks start at sysadmin, real attackers start with a bored employee and a PDF.
In this live, two-screen session there are no slides, just two terminals: one of us attacks while the other defends, in real time. We follow the whole chain, one click to catastrophe: a phished user, a foothold on a workstation, a pivot into SQL Server as a low-privilege login, and a single everyday misconfiguration that escalates us to sysadmin.
From there the data is exfiltrated and the backups burn. Then we run it backwards: the defender closes each door, often with a single line of T-SQL, until the exact same attack fails at every step.
You will leave able to name every link in the chain and the one control that cuts it. Entry-level and fast-paed: if you run, build on, or protect SQL Server, this is the hour that shows you how the breah really happens and how to stop it.
Your Database Has a New User: Threat Modelling AI Access to the Data Platform
Every AI feature your organisation ships eventually lands on your data platform. Chatbots, RAG pipelines, autonomous agents and MCP servers all show up as connections, logins and queries, but unlike human users, they write their own SQL, follow instructions from untrusted input, and can’t explain why they asked for what they did. To your database engine they look like any other session. That’s the problem.
We’ll threat-model the integration patterns DBAs now get asked to support: RAG over operational and analytical data, vector search inside the database, tool-calling agents, and MCP servers sitting in front of SQL. For each one we’ll trace the path from prompt to query plan, find where trust gets assumed, and look at what an attacker gains through prompt injection, poisoned context, over-privileged service accounts, or retrieval that returns more than it should.
The second half is controls at the layer you own: dedicated agent logins with least-privilege permissions, row-level security and masking that hold no matter what the model decides, read-only and resource-governed connections, auditing that ties every query back to a specific agent and request, and detection for anomalous agent query patterns. Practical, platform-agnostic, and built for the people who’ll be on call when the agent goes rogue.
SQL Konferenz 2027 Sessionize Event Upcoming
Data Day Edinburgh 2026 Sessionize Event
dataMinds Connect 2026 Sessionize Event
Data Saturday Holland 2026 Sessionize Event
Data Saturday Oslo 2026 Sessionize Event
Level Up Tech 2026 Sessionize Event
Data Saturday Rheinland 2026 Sessionize Event
TDWI München 2026 Sessionize Event
DataGrillen 2026 Sessionize Event
SeaQL Saturday 2026 Sessionize Event
DevConf 2026 Sessionize Event
Data Left Unattended - Amsterdam Sessionize Event
Data Saturday & Fabric Friday Holland 2025 Sessionize Event
DATA:Scotland 2025 Sessionize Event
devConf 2025 Sessionize Event
SQL Konferenz 2025 Sessionize Event
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top