
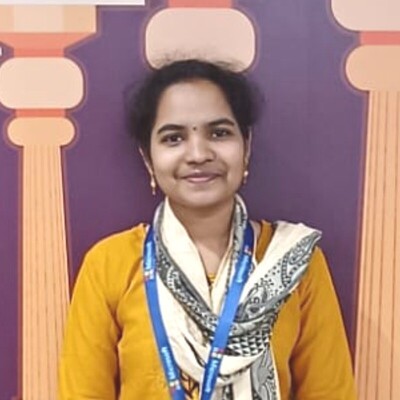
Kavya Sree Kaitepalli
Software Engineer @Microsoft
Bengaluru, India
Actions
As a Software Engineer at Microsoft, She works on building reliable and scalable software systems and enjoys solving real-world engineering problems.Kavya believes in continuous learning and improving through hands-on work. She aims to build simple, efficient, and dependable software that makes a meaningful impact.
Links
Area of Expertise
Topics
Microbots - Tiny agents to superpower your automations
Microbots is an open-source framework designed to deploy secure, lightweight AI agents ("Microbots") for autonomous code comprehension and manipulation. Addressing the critical security risks of granting LLMs access to codebases, Microbots employs a strict containerization strategy to ensure safety and control.
Key Value Propositions:
Sandboxed Security: Agents run within isolated Docker containers with explicit, least-privilege mount permissions, preventing unauthorized file system access or unintended side effects.
Specialized Agent Roles: The framework provides purpose-built bots, such as WritingBot for safe code refactoring and ReadingBot for context extraction, alongside a CustomBot interface for bespoke workflows.
Agnostic Integration: Built in Python, it integrates seamlessly with major LLM providers (Azure OpenAI, Anthropic) and local models (Ollama), making it adaptable for diverse CI/CD and automation pipelines.
Why It Matters:
Microbots enables developers to harness the power of LLMs for complex software engineering tasks—like automated bug fixing and documentation—while enforcing the rigorous security boundaries required for production environments.
Zero Trust AI Sandbox Stack
This talk explores our production-hardened approach to sandboxing agentic workloads using cloud-native container technologies.
We'll walk through our multi-layered isolation strategy:
Container-Based Sandboxing: AI agents operate exclusively within Docker containers where the original codebase is mounted read-only, preventing direct modifications to production code.
Overlay Filesystem Architecture: Overlay mounts to create ephemeral writable layers where agents can safely generate and test code changes. Modified files are extracted over the network, validated before applying to the actual codebase.
Network Segmentation: We implement strict network policies and VPN-based isolation to prevent agents from accessing unauthorized external tools, downloading potentially malicious code, or pivoting to other systems in the infrastructure.
We're currently evaluating Kata Containers for kernel-level isolation and Kata-CC to enable secure agent operations on sensitive confidential workloads.
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top