
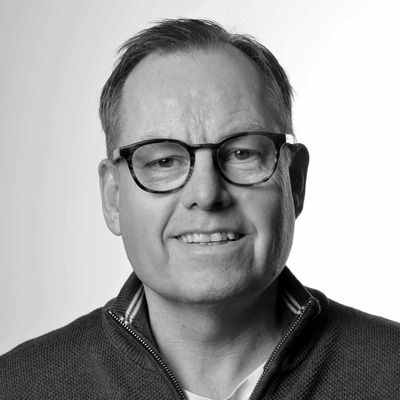
Knut Erik Hollund
Works for Bouvet in Stavanger, passioned about AppSec, developer community and Cyber Security in general.
Stavanger, Norway
Actions
Knut Erik has been engaged with coding and computing since 1983, starting with the Spectrum ZX81 and Commodore VIC20. He holds a formal education in software development. His interest in cybersecurity emerged later in his career when he played a role in establishing the Application Security (AppSec) team. This experience left a lasting impact, fuelling his desire to further enhance his cybersecurity expertise.
Currently, Knut Erik is a leader at Bouvet, where he is responsible for building and managing a team of front-end and back-end developers. Additionally, he is spearheading an initiative to develop a team of AppSec and cybersecurity engineers.
Area of Expertise
Topics
Lightning Talks 6
Lightning talks (approx 10-15 minutes each)
Talk 1: When AI writes the code, what do we do? - Tomas Hensrud Gulla
We live in a time where we can write code without understanding it. AI makes us faster, more productive, and less tired.
But what if programming isn’t just about efficiency?
What if it’s also about resistance?
Maybe the developer of the future doesn’t need to write more code. Maybe we need to play with it more.
I’ll show you examples of code written in some very different languages.
One language probably belongs on a wall. One you can’t even see. One should be performed at full volume. And the last one you absolutely cannot sit still while writing it.
This is part performance, part talk. Part humour, part serious.
Talk 2: Observability’s Sixth Sense: Detecting Anomalies in Metrics - Diana Todea
Modern systems produce more metrics than any single person can reason about. As systems grow and change, defining fixed thresholds becomes harder and unexpected behavior often appears without clearly crossing an alert boundary.
In this talk, we look at anomaly detection as a complementary way of working with metrics. Instead of relying on predefined limits, anomaly detection focuses on identifying behavior that deviates from what is normally observed over time.
Using a short, live walkthrough with real metric data, the talk shows how anomalies can surface gradual changes, unusual patterns and subtle shifts that are easy to miss in dashboards. The focus is on how developers can interpret these signals, where anomaly detection is useful and where it is not.
The session is exploratory and practical, aimed at developers who work with metrics and want additional ways to understand system behavior without introducing complex models or heavy tooling.
Talk 3: How hunting for an attack surface, led me to the front-doors of wind turbines - Knut Erik Hollund
As a relatively new in the field of cybersecurity, with a primary focus on Application Security (AppSec), I have been intrigued by the methods attackers use to identify their attack surfaces. In preparation for an internal presentation at our company, I embarked on a project to explore potential attack surfaces using various tools. My objective was to identify a wind turbine farm located in Europe. This endeavor was aimed at illustrating the Secure Design principle - "defense in depth."
During my presentation, I will guide the audience through my journey, starting from the initial question to the point where I reached the front door of the wind turbine farm. It involves tools as AI and Shodan.io.
Talk 4: Breaking the Corporate Firewall: How to get a little AI into your very large company - Sean Percival
Your company is falling behind on AI. You know it. Your competitors know it. And somewhere deep in a conference room, a committee is meeting about it — which means nothing is going to happen for another eighteen months.
This talk is not about waiting for permission.
It's about how individuals — not executives, not transformation teams, not consultants — are the ones who actually change how large organizations work. One quiet experiment at a time. One small win that can't be ignored. One person who decided to stop waiting and start doing.
"In Norway, the fastest way to do something big is to start embarrassingly small."
The corporate firewall is real. Legal will say no. IT will say no. Procurement will say nothing for six weeks and then say no. But there is a way through — and it starts with you, a low-stakes test, and a result nobody can argue with.
Why large companies stall on AI — Death by committee. The approval loop. Why "we need a strategy" means nothing is happening.
Start embarrassingly small — One team. One tool. Four weeks. One metric. Why tiny experiments are the only things that actually get approved.
Isolate the blast radius — How to ring-fence risk so legal, IT, and compliance can say yes. The sandbox framing that unlocks everything.
Show results first, ask for permission later — Why data is the only currency that moves Norwegian organizations — and how to document obsessively so the numbers do the lobbying.
How hunting for an attack surface, led me to the front-doors of wind turbines
As a relatively new in the field of cybersecurity, with a primary focus on Application Security (AppSec), I have been intrigued by the methods attackers use to identify their attack surfaces. In preparation for an internal presentation at our company, I embarked on a project to explore potential attack surfaces using various tools. My objective was to identify a wind turbine farm located in Europe. This endeavor was aimed at illustrating the Secure Design principle - "defense in depth."
During my presentation, I will guide the audience through my journey, starting from the initial question to the point where I reached the front door of the wind turbine farm. It involves tools as AI and Shodan.io.
NDC Oslo 2026 Sessionize Event
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top