
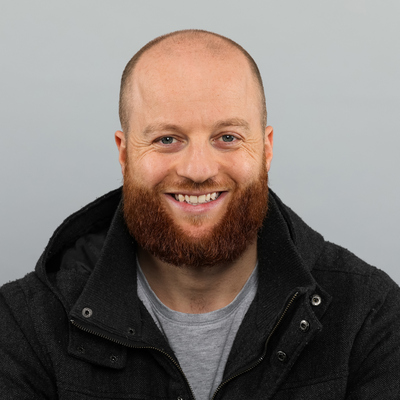
Michael Fornaro
Staff DevOps Engineer | Easygo
Melbourne, Australia
Actions
I'm an OSS enthusiast, I contribute to multiple CNCF projects and co-founded Raspbernetes & K8s@Home. I'm passionate about sharing knowledge, self-development, and inspiring the community about cloud technology's vast potential.
Area of Expertise
Topics
Streaming Under Fire
What's it like to run a platform where something is always on fire? At Kick, live streams are someone's livelihood and live has no undo, no maintenance windows, no second takes, millions watching. At that scale the happy path is a lie; traffic spikes, dependencies fail, deploys go sideways, and someone out there is always trying to knock you over. This is a war-stories talk from the team keeping it online. You'll see how we decide what "working" actually means when you can't protect everything equally.
Gitless GitOps with FluxCD
The GitOps model gave us traceable, declarative infrastructure. But relying on Git access from your clusters comes with downsides, network complexity, access control challenges, and audit gaps. This talk presents an evolved approach: keep Git as your truth, but push OCI-packaged artifacts to a registry where FluxCD can pull and reconcile securely.
You’ll learn how to: - Build and package Kubernetes manifests into OCI images with tooling like flux push or oras - Use image tags (e.g., latest, staging, stable) to decouple promotion from Git branching - Sign artifacts using keyless signatures via Sigstore (cosign) to enforce trust and verify integrity - Store and distribute SBOMs and VEX alongside manifests for audit-ready compliance - Onboard teams or tenants with minimal friction, no need to give them Git access to the cluster.
Platform Engineering: Building Fungible GKE clusters with GitOps
Discover how GitOps principles can revolutionize the way we manage GKE clusters. This talk delves into creating consistent, replicable GKE clusters using GitOps, emphasizing the power of declarative infrastructure and automated processes. Learn how to treat clusters as immutable and perform atomic upgrades and cluster life-cycle management.
Platform Engineering: Defeating the Final Boss
This talk will showcase our advanced strategies in managing and scaling Kubernetes cluster fleets using the principles of GitOps.
We'll discuss how we can use tools like FluxCD and Crossplane to automate and streamline the deployment and management of fleets of Kubernetes clusters, ensuring efficiency and reliability.
Learn about the challenges we faced and the innovative solutions we adopted in creating a robust platform that supports the dynamic needs of our engineering teams.
Our approach emphasizes the power of GitOps in achieving operational excellence, offering a blueprint for scalable, automated cluster fleet management.
Smarter security in Kubernetes with eBPF
Kubernetes gives you powerful primitives to enforce least-privilege—NetworkPolicies, Seccomp, PodSecurity—but most teams don’t use them effectively. Why? Because they’re hard to write, harder to maintain, and nearly impossible to get right without deep understanding of workload behavior. This talk explores a better approach: using eBPF to observe real runtime behavior—like syscall activity and network connections—and automatically generate policies from that data.
We’ll cover: - The challenge: why most Kubernetes workloads are over-privileged and how manual policy writing slows security adoption - The shift in mindset: from static “deny-all + guess-allow” to dynamic “observe + generate” - How eBPF helps: watching syscalls, tracking pod traffic, and surfacing actionable insights with minimal performance impact - Practical workflows: how platform and security teams can observe workloads in dev/staging, generate policies, and enforce least privilege safely - Real-world outcomes: faster onboarding, reduced blast radius, and audit-ready security posture with less manual effort
This isn’t about selling a tool. It’s about changing how we think about security in Kubernetes—and giving teams the observability and automation needed to make it real. Attendees will leave with an understanding of: - What eBPF brings to Kubernetes security - How to apply runtime data to policy generation - Why this approach aligns with compliance, platform scalability, and DevSecOps best practices
CloudCon SYD 2026 Sessionize Event Upcoming
GDG Melbourne Devfest 2026 Sessionize Event Upcoming
GDG Melbourne Devfest 2025 Sessionize Event
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top