
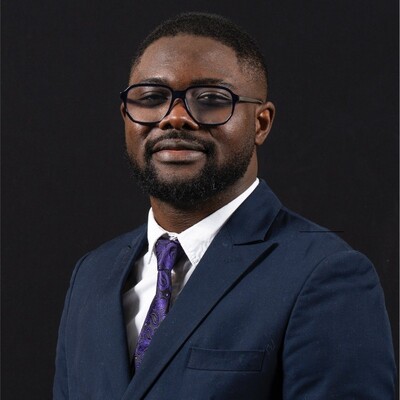
Michel Fotsing
AI Governance & Cybersecurity Architect | CISSP | ISO/IEC 42001
Architecte en cybersécurité et gouvernance de l'IA | CISSP | ISO/IEC 42001 | Auteur de l'Architecte numérique
Montréal, Canada
Actions
Michel Fotsing is a cybersecurity and AI governance architect focused on helping organizations adopt AI without losing control over security, risk, and critical decisions.
With over 11 years of experience across cybersecurity, cloud platforms, critical infrastructure, and AI-enabled systems, Michel bridges technical security and executive decision-making. He holds the CISSP credential and contributes to the ISC2 CISSP Examination Review Board.
His work explores a central question for modern organizations: How do you determine what AI can decide, what it should help decide, and what must remain under human control?
Michel developed the Three Zones framework—Automated, Augmented, and Sanctuary—to help organizations classify decisions by risk, define appropriate human oversight, and establish boundaries for AI autonomy. His approach connects AI governance principles with practical cybersecurity, risk management, and organizational accountability.
He is the author of The Digital Architect: Orchestrating Intelligence in the Age of AI and writes for an audience of technology leaders and professionals.
Michel speaks to executives, CIOs, CISOs, risk leaders, and technology teams about AI governance, cybersecurity strategy, AI risk management, and the future of human oversight. His presentations combine strategic frameworks, practical exercises, and real-world scenarios to help organizations turn abstract AI principles into actionable decisions.
Speaking topics: AI governance and accountability · ISO/IEC 42001 and AI management systems · AI risk management · Cybersecurity architecture · Human oversight of autonomous AI · Executive AI strategy.
Michel Fotsing est architecte en cybersécurité et gouvernance de l'intelligence artificielle. Il accompagne les organisations dans l'adoption de l'IA en conciliant innovation, maîtrise des risques, sécurité et responsabilité humaine.
Fort de plus de 11 ans d'expérience en cybersécurité, en plateformes infonuagiques, en infrastructures critiques et en solutions intégrant l'IA, il fait le pont entre les enjeux techniques et les décisions stratégiques des dirigeants. Titulaire du CISSP, il contribue aux travaux de l'ISC2 CISSP Examination Review Board.
Ses travaux explorent une question centrale pour les organisations : comment déterminer ce que l'IA peut décider de façon autonome, ce qu'elle doit aider à décider et ce qui doit impérativement rester sous contrôle humain ?
Michel a développé le Modèle des Trois Zones — Automatisée, Augmentée et Sanctuaire — pour aider les organisations à définir les limites de l'autonomie de l'IA, à proportionner la supervision humaine aux risques et à clarifier les responsabilités décisionnelles.
Il est l'auteur de L'Architecte Numérique : Orchestrer les intelligences à l'ère de l'IA et partage ses réflexions sur la gouvernance des systèmes hybrides humains-IA.
Ses conférences s'adressent aux dirigeants, DSI, CISO, responsables des risques, architectes et leaders de la transformation numérique. Elles combinent réflexion stratégique, scénarios concrets et outils pratiques pour transformer les principes de gouvernance de l'IA en décisions applicables sur le terrain.
Ses domaines d'intervention comprennent la gouvernance de l'IA, la gestion des risques liés à l'IA, ISO/IEC 42001, l'architecture de cybersécurité, la supervision humaine des systèmes autonomes et la stratégie de sécurité numérique.
Area of Expertise
Topics
Countering AI-Driven Threats in Cloud Environments Through Proactive Forensic en
As AI-driven threats, such as deepfakes and adversarial model attacks, increasingly target cloud infrastructures, organizations must adopt proactive forensics and robust workforce training to stay ahead. As a CISSP-certified Cybersecurity Architect at La Vie en Rose and former IT Manager leading a nine-member DevOps team at SkyVue Solutions, I’ll share actionable strategies for countering AI-driven threats in Microsoft Azure environments. This session will present two real-world case studies: a deepfake-enabled phishing campaign detected using Microsoft Sentinel and a model poisoning attempt mitigated with IBM QRadar. Attendees will learn how to leverage forensic techniques, including log analysis and behavioral anomaly detection, to identify AI-specific attack patterns. I’ll demonstrate how to integrate threat intelligence into incident response workflows, align with standards like NIST 800-61, and train teams to recognize and respond to AI threats using tools like Fortinet and Aruba Clearpass. The session will also address smart logging strategies to balance visibility with efficiency, avoiding data overload. Drawing on my experience training analysts at Polytechnique Montreal and IT students at Solhitech Sarl, I’ll provide practical frameworks for upskilling teams to handle emerging AI-driven threats, ensuring compliance and resilience. This presentation offers a forward-looking approach to securing cloud systems against the evolving landscape of AI-powered cyberattacks, empowering attendees to strengthen their defenses and workforce capabilities.
Presentation Proposal: Mitigating Adversarial AI Risks in Cloud Environments Through Proactive Foren en
As adversarial AI threats, like deepfakes and model poisoning, target enterprise cloud systems, proactive forensics and workforce training are critical to mitigate risks. As a CISSP-certified Cybersecurity Architect at La Vie en Rose and former IT Manager, I’ll share practical strategies for securing Azure-based environments against AI-driven attacks. Through real-world case studies—including a deepfake-driven phishing attempt detected with Microsoft Sentinel — I’ll demonstrate how forensic techniques (e.g., log analysis, anomaly detection) uncover adversarial tactics. Attendees will learn to integrate AI-specific threat intelligence into response workflows, align with emerging compliance standards (e.g., NIST AI RMF), and train teams to recognize AI threats. This session offers actionable insights to balance AI adoption with security, ensuring organizations stay ahead of adversarial risks in the generative AI era.
Presentation Proposal: Countering AI-Driven Threats in Cloud Through Proactive Forensics en
As AI-driven threats, such as deepfakes and adversarial model attacks, increasingly target cloud infrastructures, organizations must adopt proactive forensics and robust workforce training to stay ahead. As a CISSP-certified Cybersecurity Architect at La Vie en Rose and former IT Manager leading a nine-member DevOps team at SkyVue Solutions, I’ll share actionable strategies for countering AI-driven threats in Microsoft Azure environments. This session will present two real-world case studies: a deepfake-enabled phishing campaign detected using Microsoft Sentinel and a model poisoning attempt mitigated with IBM QRadar. Attendees will learn how to leverage forensic techniques, including log analysis and behavioral anomaly detection, to identify AI-specific attack patterns. I’ll demonstrate how to integrate threat intelligence into incident response workflows, align with standards like NIST 800-61, and train teams to recognize and respond to AI threats using tools like Fortinet and Aruba Clearpass. The session will also address smart logging strategies to balance visibility with efficiency, avoiding data overload. Drawing on my experience training analysts at Polytechnique Montreal and IT students at Solhitech Sarl, I’ll provide practical frameworks for upskilling teams to handle emerging AI-driven threats, ensuring compliance and resilience. This presentation offers a forward-looking approach to securing cloud systems against the evolving landscape of AI-powered cyberattacks, empowering attendees to strengthen their defenses and workforce capabilities.
Le Mur des 250 Millisecondes : Gouverner quand l’IA décide en 2,7 secondes fr
L’IA exécute en 2,7 secondes. Un humain a besoin de 250 millisecondes rien que pour percevoir un stimulus.
Pendant qu’un comité de direction planifie sa transformation digitale sur 3 ans, les agents IA autonomes redesignent les processus en 48 heures. Pendant qu’un CISO valide une politique de sécurité en 6 semaines, une cyberattaque automatisée exfiltre les données en 2,7 secondes.
Cette conférence révèle pourquoi la vitesse de l’IA change fondamentalement les règles de gouvernance, et introduit le Modèle des Trois Zones pour cartographier où votre organisation doit automatiser, augmenter ou sanctuariser.
Elle est inspirée de mon livre "L'architecte Numérique: Orchestrer les intelligences a l'ère de l'IA"
Vous repartirez avec une grille de décision applicable immédiatement à vos comités de direction.
Public cible : Dirigeants, DSI, CISO, VP Transformation, responsables stratégie
Format : Keynote (45-60 min) | Conférence interactive (90 min)
Le Modèle des 3 Zones : Cartographier l’orchestration humains-IA fr
Votre organisation fonctionne déjà comme un système hybride humains-IA. Mais avez-vous cartographié où l’IA doit décider seule, où elle doit assister, et où l’humain doit rester souverain ?
Le Modèle des Trois Zones est un cadre stratégique pour gouverner l’automatisation sans perdre le contrôle :
- Zone Automatisée : L’IA décide seule (tâches répétitives, faible risque)
- Zone Augmentée : Humain + IA en synergie (décisions complexes, risque modéré)
- Zone Sanctuaire : Humain souverain (irréversible, éthique, stratégique)
Cet atelier combine cas réels (cyberattaques, flash crash financier, dérives d’automatisation) et exercices pratiques pour cartographier vos propres flux critiques.
Il est inspiré de mon livre "L'architecte Numérique: Orchestrer les intelligences a l'ère de l'IA"
Public cible : COMEX, DSI, CISO, responsables produit, responsables transformation
Format : Workshop (demi-journée) | Conférence (90 min)
Le Seuil du Courage : L’éthique de l’IA décisionnelle fr
Une IA peut optimiser un processus de recrutement. Mais doit-elle décider qui embaucher ?
Une IA peut analyser des risques médicaux. Mais doit-elle décider d’un traitement ?
Une IA peut identifier des menaces. Mais doit-elle décider de contre-attaquer ?
Le Seuil du Courage explore la frontière entre automatisation efficace et décisions irréversibles. Quand délègue-t-on à l’IA ? Quand l’humain doit-il garder la main ? Et surtout : qui décide de cette frontière dans votre organisation ?
Cette conférence combine réflexion profonde, cas d’usage réels (justice prédictive, médecine, cyberdéfense) et outils concrets pour tracer votre propre Seuil du Courage.
Elle est inspirée de mon livre "L'architecte Numérique: Orchestrer les intelligences a l'ère de l'IA"
Public cible : Dirigeants, comités d’éthique, responsables conformité, DSI, juristes
Format : Conférence (60 min) | Panel / Table ronde (90 min)
ISO/IEC 42001 in Practice: From AI Principles to Operational Governance en fr
AI principles are easy to endorse. Turning them into operational controls, accountability, and measurable outcomes is the real challenge.
This session explores how ISO/IEC 42001 helps organizations establish an AI Management System (AIMS), integrate AI risk management, define responsibilities, implement human oversight, and build evidence of continual improvement.
Participants will leave with practical insights to translate AI governance principles into actionable organizational practices.
Target audience: AI governance professionals, CISOs, CIOs, risk managers, auditors, and consultants. Level: Intermediate. Preferred duration: 45–60 minutes; interactive workshop option: 90 minutes. No special technical requirements.
ISO/IEC 42001 en pratique : des principes de l'IA à une gouvernance opérationnelle en fr
Adhérer aux principes d'une IA responsable est une chose. Les traduire en contrôles opérationnels, en responsabilités claires et en résultats mesurables en est une autre.
Cette conférence explore comment ISO/IEC 42001 aide les organisations à établir un système de management de l'IA (SMIA), intégrer la gestion des risques, définir les responsabilités, assurer la supervision humaine et démontrer l'amélioration continue.
Les participants repartiront avec des pistes concrètes pour transformer les principes de gouvernance de l'IA en pratiques organisationnelles applicables.
Public cible : professionnels de la gouvernance de l'IA, CISO, DSI, gestionnaires des risques, auditeurs et consultants. Niveau : intermédiaire. Durée souhaitée : 45 à 60 minutes ; possibilité d'un atelier interactif de 90 minutes. Aucun besoin technique particulier.
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top