
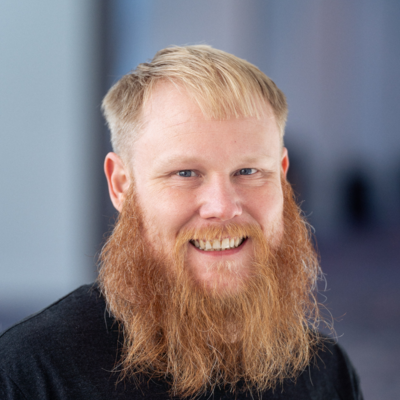
Mike Conrad
Making software a strategic deterrent
Chattanooga, Tennessee, United States
Actions
Mike Conrad is a platform engineer at Defense Unicorns, where he works on secure, portable deployment tooling for mission-critical environments. He's spent the better part of a decade helping teams understand that platforms should make developers faster, not create new obstacles. He's passionate about Kubernetes, open source, and building things that work the same way whether they're running in a data center or on a laptop. He's a Golden Kubestronaut, holds multiple Azure certifications, and has a habit of finding security gaps in places nobody thought to look.
Badges
Area of Expertise
Topics
Demystifying Docker: A Beginner’s Guide to Containerization and Beyond
Docker is a powerful tool for developers, but getting started can feel overwhelming. In this session, we’ll break down Docker concepts and commands in a way that’s accessible to beginners and intermediate developers alike. Whether you’re looking to containerize your local development environment or understand how to deploy containers in production, this talk will give you the knowledge you need to get started and avoid common pitfalls.
We’ll begin with the basics, walking through essential Docker commands, then move on to practical steps for creating and managing containers. You’ll learn how to containerize your development environment, making your workflows more efficient and portable. From there, we’ll explore Docker’s deployment options for production environments, highlighting the nuances and gotchas that often catch new users by surprise.
We'll also dive into Docker Swarm mode for orchestration and explore advanced troubleshooting techniques to help you resolve container-related issues with ease.
This talk is perfect for developers who are looking to understand Docker more deeply and expand their containerization skills, whether you're just getting started or aiming to fine-tune your knowledge for more complex use cases.
Prerequisites: Basic understanding of software development concepts and a desire to learn about containerization. No prior Docker experience is required, but familiarity with the command line will be helpful.
Homelab-in-a-Box: Self-Hosting with the Unified Defense Stack
Shipping a secure, portable platform shouldn’t require a cloud account, a giant budget, or weeks of yak-shaving. In this session we’ll build a “Homelab-in-a-Box” using Unified Defense Stack (UDS) Core: a FOSS secure runtime platform that simplifies delivery and deployment of apps across environments while integrating the security needed for authorization.
We’ll walk through a repeatable workflow for self-hosting: from a clean machine to a working local environment you can demo, iterate on, and eventually scale up. Along the way we’ll highlight how UDS enables portable artifacts, reduces vendor lock-in, and makes it easy to update bundles/packages on demand.
Expect a fast tour of the mental model (packages/bundles + secure platform layers), a real homelab-friendly deployment story, and hard-earned tips for making local environments behave like “real” production.
Homelab Hero: Deploying a Secure, Production-Ready Media Server with UDS
Bring the power of production-ready, secure infrastructure to your home! In this 4-hour hands-on workshop, we will demystify the Unified Defense Stack (UDS) by building a fully functional homelab environment.
We’ll start by setting up a server with UDS Core, establishing a robust foundation based on zero-trust principles. From there, participants will learn the "Defense Unicorns way" of packaging applications by building and deploying a custom UDS package for Plex Media Server.
By the end of this session, you’ll understand the advantages of an open-source, secure-by-default stack and gain the practical skills needed to create, bundle, and deploy your own applications using UDS. Whether you're an automation specialist or a homelab enthusiast, you'll leave with a production-ready template for your home projects.
What to bring:
Participants will need a laptop with a modern web browser and a container platform such as Docker, Podman, etc.
Participants should ensure that their machine meets the minimum requirements as outlined here: https://uds.defenseunicorns.com/getting-started/basic-requirements/
Hidden in Plain Sight: Certificate Transparency and the Logs Nobody Told You About
Most engineers know TLS certificates exist. Few know that every certificate ever issued is recorded in a public, searchable, append-only log, and that anyone can search it.
Certificate Transparency was designed to improve the security of the web's certificate infrastructure. As a side effect, it creates a permanent public record of infrastructure that developers often assume is private. That staging environment with no authentication. That internal tool on an obscure subdomain. That dev portal behind a domain nobody was supposed to know about.
Security by obscurity has always been a weak strategy. CT logs make it a nonexistent one.
In this session we'll cover how Certificate Transparency works, why it exists, and what it means for anything you've ever deployed behind a TLS certificate. We'll use real search tooling to find exposed infrastructure live, walk through two real examples of sensitive services discovered this way (including one that was responsibly disclosed and quietly taken down), and end with a practical framework for auditing your own domains before someone else does.
You'll leave knowing how to search CT logs, what to look for, and how to make better decisions about what should and shouldn't have a public certificate attached to it.
Talk Outline
1. What TLS certificates are (60-90 seconds, just enough context)
2. What Certificate Transparency is and why it was created
3. How CT logs work (append-only, public, monitored by browsers)
4. Live demo: searching CT logs with [driftnet.io or similar]
5. Real example 1: exposed dev portal, no authentication, sensitive data, responsible disclosure
6. Real example 2: newspaper platform, paywall-free developer version publicly accessible
7. What this means for engineers: every cert is a breadcrumb
8. Practical framework: audit your own domains now
Scenic City Summit 2026 Sessionize Event
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top