
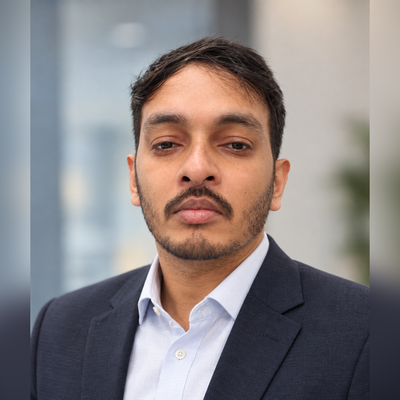
Niladri Sekhar Hore
F50 - Manager - Threat Detection & Applied Intelligence (AI / ML)
Bengaluru, India
Actions
With more than a decade across data engineering and cybersecurity, Niladri is a security engineering leader currently serving as Manager, Threat Detection and Applied Intelligence at StoneX Group, a Fortune 50 financial services firm. He owns the strategy, roadmap, and delivery for how the organization detects, investigates, and responds to threats — strengthening cyber defense, deepening observability, and building secure, scalable data and AI systems. His career spans global organizations including Cognizant, Eli Lilly, Accenture, and KPMG, where he led initiatives across eDiscovery, digital forensics, GRC, security engineering, and cloud engineering.
Blending deep technical expertise with strategic direction, he works at the intersection of data, threat operations, and governance — turning security operations from a manual, alert-driven function into an AI-native, evidence-driven discipline. His recent work spans synthetic media abuse and deepfake detection, adversarial AI in enterprise settings, and the production of machine-learning models and real-world AI systems that solve tangible business problems — underpinned by strong command of AI guardrails and model-exploitation protection, built human-in-the-loop and governed to OWASP LLM Top 10 and NIST AI RMF.
Links
Area of Expertise
Topics
Non-Human Identity Crisis: AI Agents as Unaccountable Actors in Enterprise Security
Abstract:
As AI agents become embedded in enterprise systems, they are increasingly performing actions traditionally associated with human users and service accounts—accessing data, invoking APIs, and executing workflows. However, these agents do not fit cleanly into existing identity and access management (IAM) models, creating a fundamental gap in how organizations enforce accountability, authorization, and auditability.
This talk introduces the concept of the “non-human identity crisis” in AI agents, where autonomous systems operate with delegated authority but without clear identity boundaries. We explore how AI agents blur the line between user intent and system execution, leading to ambiguous ownership of actions and breakdowns in traditional security controls.
Through practical scenarios, we demonstrate how AI agents leverage shared credentials, inherited permissions, and implicit trust to perform actions that cannot be easily attributed or governed. These challenges impact core security functions, including access control enforcement, audit logging, incident response, and compliance reporting.
The session analyzes how existing IAM frameworks—designed for humans and deterministic services—fail to address the dynamic and context-driven behavior of AI agents. We highlight gaps in identity propagation, session context, and authorization enforcement when decision-making is delegated to LLM-driven systems.
To address these challenges, we propose a set of design principles for managing AI agents as first-class identities. This includes binding user context to agent actions, enforcing explicit authorization at execution points, and enhancing audit trails to capture intent, decision flow, and action outcomes.
This talk provides a new lens for understanding AI agent security—not just as an application risk, but as a fundamental identity and trust problem that requires rethinking how enterprises model and secure non-human actors.
Key Takeaways:
1. Why AI agents do not fit into existing IAM and identity models
2. How lack of identity boundaries creates security and audit gaps
3. Challenges in attributing actions and enforcing accountability
4. Impact on compliance, logging, and incident response
5. Design principles for managing AI agents as secure, auditable identities
Session Format:
Technical and architectural deep dive with real-world scenarios.
Detection Engineering for AI Agents: Building SOC Visibility into Autonomous Systems
Abstract:
As AI agents become embedded across enterprise environments—interacting with internal systems, executing actions, and making autonomous decisions—they introduce a new and largely unmonitored attack surface. While much of the current focus in AI security is on preventing prompt injection and model manipulation, far less attention has been given to a critical question: how do we detect when an AI agent is being abused?
This talk presents a practical approach to detection engineering for AI agents, focusing on how security operations teams can gain visibility into autonomous systems and identify malicious or unintended behavior. Drawing from real-world architectures, we explore how AI agents interact with tools, APIs, and cloud services, and how these interactions can be instrumented, logged, and analyzed using existing security monitoring frameworks.
Through a series of realistic scenarios, we demonstrate how compromised or manipulated agents exhibit observable patterns—such as anomalous tool usage, unusual data access, and unexpected outbound communication—that can be detected using telemetry pipelines and SIEM-based analysis. Attendees will see how to translate agent activity into actionable security signals and build detection logic aligned with modern SOC practices.
The session also highlights the limitations of current logging and monitoring approaches, showing why traditional application telemetry is insufficient for agentic systems. We introduce a structured model for capturing agent behavior, including input/output tracing, tool invocation auditing, and context-aware event correlation.
Finally, we present practical strategies for implementing detection and response capabilities for AI agents, including alerting on high-risk behaviors, integrating agent telemetry into existing security workflows, and designing agents with observability in mind.
This talk bridges the gap between AI security research and operational security, equipping defenders with the tools and frameworks needed to monitor, detect, and respond to threats in autonomous AI systems.
Key Takeaways:
Why AI agents create a new blind spot for security operations
How to instrument and log AI agent behavior effectively
Detecting anomalous tool usage, data access, and agent-driven actions
Building SIEM detections and telemetry pipelines for agent activity
Practical approaches to integrating AI agents into existing SOC workflows
Session Format:
Technical deep dive with real-world scenarios and detection-focused demonstrations.
Niladri Sekhar Hore - The Deepfake Supply Chain
In an era where synthetic media and deepfakes are becoming tools of choice for adversaries, this session delivers a deep dive into the entire lifecycle of a synthetic media attack—from initial OSINT gathering to monetization through fraud and extortion. Drawing from real-world incidents, cutting-edge research, and red-team simulations, we’ll dissect how deepfake-based attacks are operationalized, bypass controls, and reshape the threat landscape across sectors.
Finally, the session presents a comprehensive defense framework—covering AI-driven detection techniques, content authenticity infrastructure (C2PA), security engineering controls, and organizational playbooks for executive impersonation response. By the end of this session, security professionals, risk leaders, and technical architects will be equipped with actionable strategies to detect, disrupt, and defend against synthetic media threats in the real world.
Blue Team Con 2026
Behaviour Driven Detection for Software Supply Chain Exploitation
Abstract
Modern software development depends on an intricate ecosystem of open‑source libraries, third‑party services, CI/CD workflows, container registries, package repositories, and cloud‑native infrastructure. As organizations accelerate development velocity, their applications increasingly rely on components they neither wrote nor control. This creates a supply chain environment where the weakest external link becomes the attacker’s easiest entry point. While Application Security (AppSec) teams focus on code reviews, SAST/DAST, SCA results, and secure SDLC controls, many of the most dangerous threats originate outside their visibility. These include malicious dependency updates, compromised package maintainers, poisoned CI/CD pipelines, hijacked SDKs, and third‑party API breaches—risks that traditional AppSec tooling isn’t designed to detect.
At the same time, Cyber defence teams track adversary activity, ecosystem‑level manipulation, suspicious code commits, dark‑web chatter, targeted campaigns against popular libraries, and exploitation of software supply chain dependencies. They see indicators and emerging threats far earlier than any automated scanner—but this intelligence rarely makes its way into AppSec decision‑making. As a result, AppSec teams continue to approve dependencies with no CVEs, unaware that the maintainer was compromised; security testing pipelines approve builds even though TI has already flagged one of the upstream components; and organizations ship production code containing malicious logic that no scanner will ever detect because the code behaves "as designed"—just not by your design.
This talk presents a unified model for bridging these gaps—delivering a strategic approach through supply chain defence. Attendees will learn how real‑world supply chain attacks unfold, why they bypass traditional AppSec controls, and how integrating cyber defence changes the defender’s perspective. We break down practical detection methods for ecosystem‑level anomalies, maintainer compromise signals, malicious package patterns, CI/CD infiltration attempts, and signs of upstream component manipulation. Through real attack examples and defensive case studies, we show how organizations can fuse AppSec findings (SCA results, dependency mapping, SBOM data) with cyber defence to build an adaptive, intelligence‑driven supply chain protection strategy.
Key Takeaways
Why AppSec alone cannot detect supply chain compromise — and the specific blind spots hidden inside package ecosystems, CI/CD pipelines, and third‑party integrations.
A practical integration model where AppSec and Cyber defence team jointly monitor, validate, and block risky dependencies or services before they reach production.
Field-tested workflows for real-time supply chain monitoring using SBOM enrichment, threat feeds, dependency risk correlation, and behaviour-based anomaly detection.
A blueprint for building an enterprise supply chain defence program that continuously adapts to attacker evolution, ecosystem shifts, and vendor risks.
Why This Talk Is Important
Supply chain attacks are now a preferred strategy for both state-sponsored and financially motivated threat actors. They exploit trust relationships between developers, automation systems, and ecosystem maintainers—areas where AppSec with cyber defence team lacks visibility with limited operational influence. This session provides a practical, actionable roadmap for bringing both teams together to defend the modern software supply chain—before adversaries weaponize it.
https://blueteamcon2026.sched.com/speaker/niladrisekharhore
CODE BLUE 2025 Sessionize Event
Niladri Sekhar Hore
F50 - Manager - Threat Detection & Applied Intelligence (AI / ML)
Bengaluru, India
Links
Actions
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top