
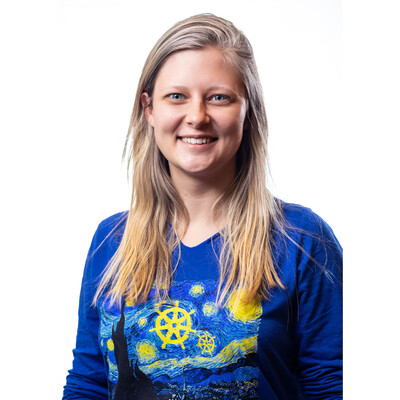
Nina Polshakova
Member of Technical Staff
Actions
Nina is a software engineer working on AI Gateway inference projects. She contributes to open source projects, including Kubernetes, Istio, kagent, agentgateway, and kgateway. A CNCF Ambassador and former Kubernetes v1.33 Release Lead, she’s also a member of the Cloud Native AI Working Group and has co-authored papers on AI security. She enjoys exploring new open source projects and building AI agents—ideally so they can do her job for her. 🤖
Hacking Istio: The Good, The Bad, and The Misconfigured
Istio provides out-of-the-box network security tools- from mutual TLS (mTLS) encryption to powerful AuthorizationPolicies for access control. However, misconfigurations can expose vulnerabilities, compromising the security of the entire mesh. The new Ambient mode in Istio removes the need for sidecars but requires new considerations when configuring access control at different network layers.
The tutorial will provide Kubernetes clusters with Istio installed and some vulnerabilities ready for you to exploit and learn from. After an introduction to Istio, we will provide time for participants to find and exploit the Istio misconfigurations (with hints if you get stuck!). We will wrap up the tutorial by walking through the steps to find the flag hidden on the cluster.
This is a beginner-friendly, hands-on, collaborative tutorial to learn the importance of correctly configuring Istio security policies and what can go wrong if misconfiguration slips through the cracks.
Speak Egress and Exit: A Look at Securing Traffic Out of the Mesh with Istio
Your service mesh is up and running, but now your request must venture securely beyond the mesh!
On top of defining multiple CRs (ServiceEntries, Gateways, VirtualServices, DestinationRules, oh my!), you’ll need to consider the routing and security configurations for egress traffic that Istio supports: sidecar TLS origination, egress gateway TLS origination, TLS passthrough, ExternalName Services, and more!
Though Istio can send traffic to an external IP address, hostname, or internal DNS entry directly, this doesn’t limit which services can access external endpoints. Egress gateways enforce policies across an organization and provide a centralized point for monitoring, controlling, and shaping outbound traffic.
In a live demo, we’ll build up Istio configuration piece by piece for setups simple to complex and peek behind the scenes at the underlying Envoy configuration. Together we’ll deliver a request out of the cozy, hobbit hole mesh and into the fiery chasm of the outside world.
No Mess Rollouts with Gatewa: Leveraging Gateway API and ArgoCD for Progressive Application Delivery
Modern application delivery is filled with pitfalls: version transitions, traffic management, performance monitoring, and rollback mechanisms. If you encounter a problem during an upgrade, what can you do? Mirror traffic? Debug locally? Roll back?
A common Gateway API enables any provider to support Argo Rollouts without any custom ad-hoc code. ArgoCD monitors Prometheus metrics to verify the performance of a new version and reverts to the previous version if the metrics don't meet success criteria.
This hands-on lab will guide you on how to integrate Argo Rollouts with applications running different Gateway API implementations. Utilizing ArgoCD and Gateway API resources (HTTPRoute), you’ll learn to adjust traffic weights and gradually direct more traffic to a new version.
The lab will also explore challenges in route delegation and role-based access control within the Gateway API and potential extensions to address gaps in traffic shaping, access control, and debugging rollouts.
Kubeflow & Istio, a perfect match! Investigating Istio’s Role in MLOps
When operating Machine Learning workflows there are many moving pieces that are required to serve ML models. When models change, it is challenging to generate the logic for shifting to a new model, while ensuring that security and resiliency is maintained.
If using Kubeflow and KServe, things that need to be considered such as security, routing, and observability, are abstracted away. Under the hood, Istio is doing all the heavy lifting, handling the configuration needed for everything from security with AuthN and AuthZ policies to canary deployments.
We will cover topics including:
- How Istio can help with exposing existing and canary releasing newer models.
- The minimum viable Istio configuration to allow for secure ML operations.
- How KServe’s CRs are translated into Istio resources
- Configuration for traffic mirroring, fault injection, failover, rate-limit, external authentication, and BYO wasm plugins with Istio alongside the generated Kubeflow and KServe configurations
Testing Istio’s Virtual Machine integration locally with Calico
Istio provides native Virtual Machine integration for legacy applications which requires IP connectivity to the East/West gateway deployed in the mesh, and optionally connectivity to the pod networking for enhanced performance.
In production deployments, the communication between Kubernetes nodes and non-Kubernetes nodes are often handled with sophisticated techniques like VPC or VPN, but on a developer machine your Kubernetes nodes may be running in a simulated environment such as minikube, k3s or kind. It can be tricky to test this locally on a developer setup. How can you test calls from a Kubernetes service locally to and from a service on a VM without using LoadBalancer type Kubernetes services - using only Cluster-IP or Pod-IP?
In this session, I will talk about challenges you may face in a developer setup and how using the Calico Networking Plugin enables you to develop VM integrated meshes without LoadBalancer services in both single network and multi network environments.
Pi in the Sky: Onboarding Edge Workloads into the Service Mesh!
A range of industries including industrial automation, smart appliances, robotics, and agricultural systems require edge computing. What if there was a way to abstract networking policies, security, and observability from the application running on the edge? Enter Istio. Istio supports connecting workloads outside of a K8s to the mesh providing the benefits of a service mesh to workloads running anywhere- from legacy applications running on ec2 instance to a tiny Raspberry Pi. Connecting workloads with the new Istio Ambient model simplifies the process of adding edge devices into the mesh- without any messy sidecar. We’ll use a Raspberry Pi and onboard it into the Mesh, proving out edge computing use cases.
In this talk, we illustrate seemingly endless possibilities with how Ambient Mesh can support Edge Compute environments without any changes to the underlying applications and provides unified L3/L4 Network policies, security, and observability.
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top