
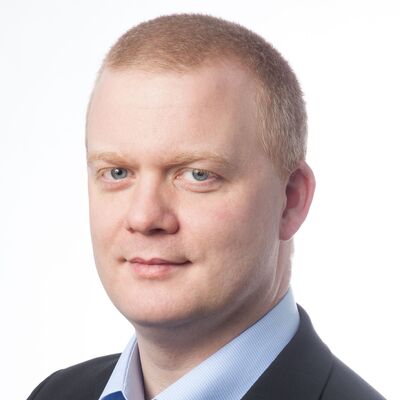
Per-Torben Sørensen
MVP Identity & Access, Senior Architect at SoftwareOne, MCT and founder of agderinthe.cloud
Kristiansand, Norway
Actions
Per-Torben Sørensen is a Microsoft MVP in Identity & Access and Senior Architect at SoftwareOne, with 27 years in IT. He works on Microsoft Entra and Microsoft 365 security: Conditional Access, passwordless authentication with passkeys, and joining identity with Microsoft Purview into a Zero Trust approach that holds up in the Copilot era. His sessions are demo-heavy and grounded in real deployments. He is an MCT, runs agderinthe.cloud, and has spoken at Experts Live, Scottish Summit, NIC and Workplace Ninjas.
Badges
Area of Expertise
Topics
The Zero Trust Power Couple, Why Identity Without Data Protection Is Just Half a Marriage
Zero Trust has been the industry mantra for years, but most implementations still stop at identity. Conditional Access policies guard the front door, yet once a user is authenticated, data moves freely across endpoints, apps, and AI tools. In 2026, that gap is no longer theoretical. It is operational risk.
This session explores why identity-only Zero Trust fails in Copilot and AI-driven environments, and how Microsoft Entra and Microsoft Purview together form a continuous control loop. We will walk through how Entra decides who gets access, how Purview decides what they can do with the data, and why AI finally makes these policies matter.
Attendees will learn how sensitivity labels act as policy anchors, how identity context enriches data protection decisions, and how DLP and adaptive protection close the gap between authentication and authorization. We will demonstrate how the same user with the same identity gets radically different Copilot outcomes depending on labels and data policies.
You will leave with a practical architecture pattern for Zero Trust that survives oversharing, AI acceleration, and the uncomfortable truth that authenticated does not mean authorized for data use.
No more identity theft! Harden your identity security today
This session is a level 300 session designed to provide a comprehensive understanding of how to enhance the security of Entra ID using Conditional Access and passkeys. The session begins with an overview of Entra ID, a robust identity management solution, and the importance of identity security in the current digital landscape.
The focus then shifts to Conditional Access, a critical component in maintaining security. Participants will learn how Conditional Access works and how it can be leveraged to strengthen Entra ID security. The session will delve into the steps for hardening Conditional Access, providing participants with practical knowledge they can apply in their organizations.
The session also covers the use of passkeys as an additional layer of security. Participants will learn how passkeys can be integrated with Entra ID and Conditional Access for enhanced security and perhaps even a passwordless solution.
Urgent access without security compromise!
Disasters don't wait until it is convenient; they strike when you're busy or unavailable! So let us show you how Microsoft Entra and Microsoft Purview can work together and form a highly secure access solution, which is flexible enough to provide temporary access in times of crises.
Hold onto your access tokens! Per-Torben is packing his bags and heading to sunny Spain. But while he is sipping sangria, disaster strikes back home in Norway, and suddenly he needs to step in and this requires immediate access to a top secret project. But surely we can't give him access to this incredibly sensitive project without compromising our security posture! Or can we?
In this session, Åsne Holtklimpen and Per-Torben Sørensen explains how Microsoft Entra and Microsoft Purview can work together and form a highly secure access solution which is flexible enough to provide temporary access from sunny Spain in a time of crisis.
We will explain and demo:
* How Conditional Access policies and Access Packages provide flexible geo-filtering for your environment
* How sensitivity labels can tap into Conditional Access policies and together they can be your best travel companions
* Why Microsoft Information Protection (MIP) is the (sun)screen your data needs, no matter where in the world you are.
Passkey Passion: Proper Planning Prevents Poor… Authentication
Passwords are dying. Microsoft is already moving users toward passkeys, whether organizations are ready or not.
This means organizations are being forced to rethink onboarding, recovery, Conditional Access, and user experience. The question is no longer if you will deploy passkeys. It's whether you'll be ready.
In this session, we'll cut through the marketing and look at how passkeys actually work in Microsoft Entra ID. You'll learn when to use device-bound versus synced passkeys, how passkey profiles and attestation affect your design and why onboarding often breaks in real tenants. More importantly, you'll learn how to make the right architectural decisions before your rollout locks you into choices that are difficult to reverse.
Expect live demos, real-world deployment lessons, and a few strong opinions from the trenches. We'll cover Temporary Access Pass, Conditional Access, registration campaigns, passkey providers, guest access, recovery strategies, and Microsoft's rapidly evolving roadmap.
You'll leave with a practical framework for planning and deploying passkeys in production, plus a checklist of mistakes to avoid before your users, admins, and help desk find them for you.
Level 300
Assumes familiarity with Microsoft Entra ID, Conditional Access, and modern authentication concepts.
The Chain Breaker: Eliminating Weak Links in Conditional Access
Conditional Access is often described as the last line of defense for your identities. The problem is that most environments contain weak links that quietly undermine the entire design.
A forgotten service account. Legacy authentication. Weak MFA methods. Coverage gaps. An administrator who can modify Conditional Access without oversight. Any one of them can become the opening an attacker needs.
In this live, demo-driven session, we'll take a Conditional Access environment with all the usual weaknesses and see if we can eliminate every weak link before time runs out.
Starting with break-glass accounts and tenant safety, we'll build a secure Conditional Access architecture from the ground up. Along the way we'll implement a block-by-default strategy, create persona-based access controls, handle exceptions without creating security holes, and protect Conditional Access administration using Restricted Management Administrative Units (RMAU) and delegated roles.
Whenever a design decision requires explanation, we'll stop and discuss the reasoning, trade-offs, and common mistakes behind it. The focus is not on clicking buttons. It's on understanding why Conditional Access architectures succeed or fail.
You'll leave with a practical framework for identifying weak links in your own environment, along with a proven blueprint for building a Conditional Access architecture that remains secure as it grows.
Level 300
Assumes familiarity with Microsoft Entra ID, Conditional Access, and modern authentication concepts.
Demo-heavy, requires a basic understanding of Conditional Access and authentication in Entra.
Experts Live Sweden 2026 Sessionize Event
MVP-Dagen 2026 Sessionize Event
Scottish Summit 2026 Sessionize Event
Workplace Ninjas Norway 2026 Sessionize Event
NIC Rebel Edition Sessionize Event
India Cloud Security Summit 2025 Sessionize Event
Workplace Ninjas Norway 2025 Sessionize Event
NIC Empower 2024 Sessionize Event
Experts Live Kenya 2024 Sessionize Event
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top