
Session
"I Own your Cluster" -Taking over AWS EKS cluster with Chain Attack
### Abstract
This presentation explores a research that reveals serious flaws in the AWS Elastic Kubernetes Service (EKS). We will examine two security issues in this session that could affect thousands of EKS clusters and pose serious security risks and the attack methodology I have developed for this service. Will talk about a chain attack that takes advantage of these flaws to take over K8s node and clusters, exposing the risk of unauthorized access and data compromise in Kubernetes environments on AWS.
In this session, we'll talk about how attackers with restricted access can bypass security measures, breach secured pods, and access privileged KubeAPI.
After that, we will analyze the AWS EKS architecture to highlight the vital parts that enable these attacks. You will learn about the intricacies of the attack chain and how it takes advantage of the AWS cloud infrastructure.
### Presentation Description
In this revealing session, Chen Shiri presents new research exposing high risk security issues within AWS Elastic Kubernetes Service (EKS). Titled "AWS Chain Attack - Thousands of Vulnerable EKS Clusters," this research identifies two zero-day vulnerabilities that compromise the fundamental pod isolation mechanisms in AWS EKS. These vulnerabilities grant attackers with limited initial access the capability to bypass existing security controls, directly interacting with privileged Kubernetes APIs and risking exposure of sensitive data.
Attendees will gain an in-depth understanding of:
• Critical Vulnerabilities: Detailed analysis of two zero-day vulnerabilities allowing attackers to breach pod isolation and escalate privileges.
• Implications: Comprehensive examination of the severe potential impacts, including unauthorized data access, regulatory non-compliance, financial damages, and reputational harm to affected organizations.
• Chain Attack Methodology: Introduction to an innovative attack methodology leveraging AWS instance metadata, Kubernetes functionalities, and AWS-specific mechanisms to infiltrate and control entire clusters and connected cloud resources.
• Live Proof-of-Concept Demonstration: Presentation of a compelling live demo illustrating the step-by-step execution and severity of this attack, reinforcing the urgency for immediate remediation.
Technical Deep-Dive Includes:
• Instance Metadata Exploitation: Techniques for leveraging EC2 instance metadata, exploiting VM roles accessible via Kubernetes containers to obtain sensitive cloud environment details and temporary tokens.
• Kube-Config Manipulation: Methodology for generating malicious Kube-Config files to interact with and exploit Kubernetes APIs, uncovering internal cluster structures and configurations.
Pod Access and Container Breakout: Strategies to circumvent Role-Based Access Control (RBAC), enabling attackers to escalate from compromised containers to node-level access, fully exposing all containers, secrets, and authentication credentials.
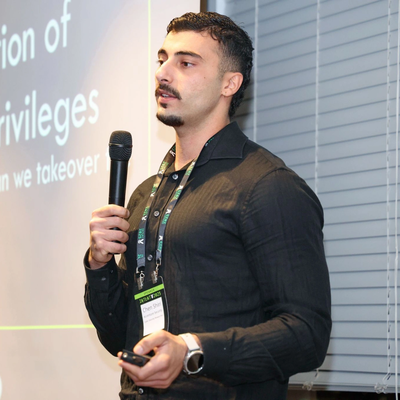
Chen Shiri
Cyber Security Researcher, Accenture Security
Tel Aviv, Israel
Links
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top