
Session
A tag to rule them all: Using tags to enumerate cloud resources
Infrastructure Enumeration is the process of gathering information about a target, after gaining initial access. That information is important for further compromising of the infrastructure. Enumeration depends on the level of privileges an attacker gets on the initial compromise. For AWS, privileges are split by API call, so if an identity can has a policy that can only execute `iam:ListUsers`, they are not allowed to execute any other API call except for it (and `sts:GetCallerIdentity`, but that is allowed by default to all identities).
To enumerate resources, an identity will need to know what access they have on the account and then know how what resources can be accessed. Due to how AWS Manages privileges and API Calls, this will result in many failed attempts and logs generated, which might tip off a defender.
In this talk, we will see how an attacker can utilize Resource Tags and only one API call to enumerate AWS Resources.
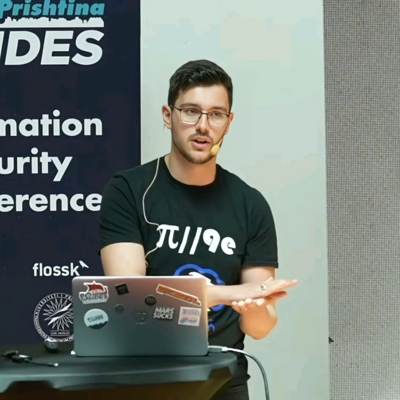
Bleon Proko
Cloud Security Researcher
Boston, Massachusetts, United States
Links
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top