
Session
Microsoft 365 Security by Design: Purview, Entra, Defender, and Copilot
Securing Microsoft 365 is no longer about configuring individual security products. As organizations expand their use of Copilot, agents, unmanaged devices, and hybrid collaboration, they need an integrated security architecture that connects identity, endpoint access, information protection, threat detection, and compliance.
This session demonstrates how Microsoft Entra ID, Intune, Defender, and Purview can work together to establish practical security guardrails across Microsoft 365.
We will explore Conditional Access, managed application protection, sensitivity labels, Data Loss Prevention, external sharing restrictions, and monitoring controls through an enterprise scenario. Particular attention will be given to balancing strong protection with usable collaboration and AI-enabled productivity.
Attendees will learn how to translate security requirements into deployable policies, validation procedures, evidence artifacts, and clearly assigned responsibilities.
Attendee takeaways
- Map common enterprise risks to Microsoft 365 security controls.
- Understand how identity, device, and data protection policies reinforce one another.
- Build an implementation plan with control owners and audit evidence.
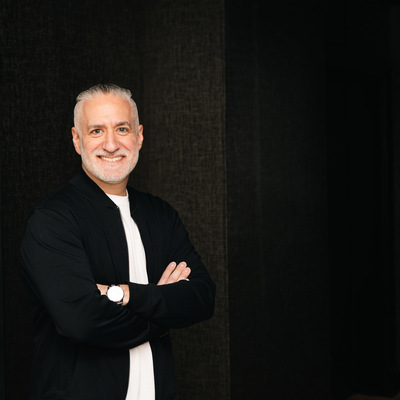
Eric Riz
Principal Consultant, eMark Consulting
Miami, Florida, United States
Links
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top