
Session
Securing RAG Applications: Threats. Mitigations. Strategies
When a seemingly safe PDF surfaced malicious commands via an LLM, we realized the problem wasn’t just prompt injection—it was everything upstream. This session walks through how we secured a Retrieval-Augmented Generation (RAG) pipeline from ingestion to inference, using AWS-native tools to detect hidden threats, filter unsafe content, and protect sensitive data in real time.
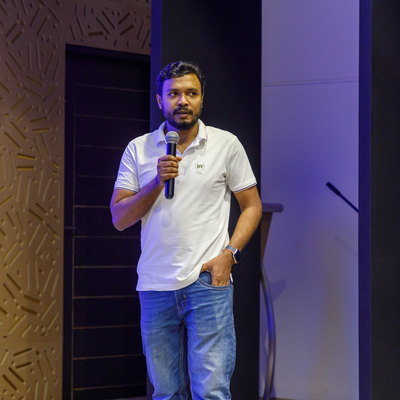
Md. Mostafa Al Mahmud
AWS Community Builder, Senior software engineer, solutions architect, public speaker, and technical writer.
Bochum, Germany
Links
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top