
Session
From 169 Minutes to 12: Where AI Pays Off in the SOC, and Where It Quietly Manufactures Risk
Every security vendor now claims AI. Few can show what it changed on an ordinary Tuesday. At Léargas Security, we built AI-assisted alert enrichment and triage into a detection platform that unifies endpoint, cloud, identity, network, and threat-intelligence data, and cut median alert resolution from 169 minutes to 12 across more than 20,000 alerts a month. This session is the field report: what we automated, how we measured it, and where a human still has to stay in the loop.
It is also the cautionary half. Automation can hide detection gaps, deskill analysts who stop reading raw evidence, and open new attack surface as AI agents gain tools, data access, and identities of their own. Drawing on ongoing research into agentic AI abuse and detection chaining, I will walk through the failure modes worth testing for and the guardrails that matter, from prompt injection and data leakage to identity boundaries for autonomous agents.
Attendees leave with a practical scorecard for evaluating AI in security operations, a short list of metrics that prove value without hiding risk, and governance language leadership will actually follow. No product pitch.
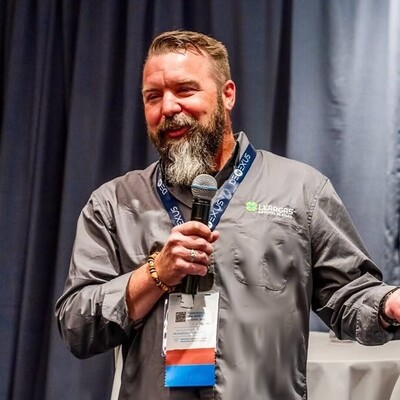
Patrick Kelley
CISO & Founder, Critical Path Security and Léargas Security | Author, The First 90 Days as CISO | RSAC 2025 Top-Rated Speaker
Atlanta, Georgia, United States
Links
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top