
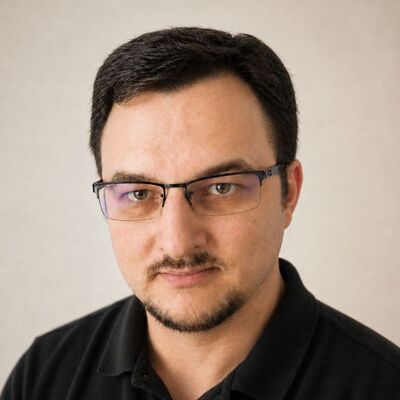
Tudor Damian
Cybersecurity, AI & Cloud Advisor @ D3 Cyber
Cluj-Napoca, Romania
Actions
Tudor Damian is a Certified Ethical Hacker and Microsoft MVP with 20+ years in IT. In his day-to-day role, he advises advises organizations on Cybersecurity, AI and Cloud governance - aiming to help them improve their security posture, and move them past “paper tiger” compliance.
His current focus is on what AI does to three things: how people think, how systems get attacked, and how the world is governed. He often speaks about cognitive surrender and the erosion of judgment, AI agents running real intrusions, and the gaps in the rules meant to contain it. Throughout hundreds of talks and trainings, the goal has always remained the same: helping IT professionals make sound decisions on AI-driven threats, post-quantum cryptography, Zero Trust, and the move from traditional software development to the probabilistic world of AI development and the security challenges that come along with it, all under a growing pile of EU regulation.
Badges



Area of Expertise
Topics
EU Laws under One Control Set: Ending the Compliance Pile-Up
NIS2, DORA, the AI Act and the CRA each come with their own deadlines, their own auditors and their own fines, and they are all landing on your desk at once, forcing you to revise your plans and timetables.
Most companies run a separate program per law: separate owner, evidence, audit, the same control tested four times, and it still misses where the requirements disagree. We'll map where one piece of evidence satisfies several EU directives and regulations at once. A handful of controls cover most requirements, and ISO 27001, ISO 42001 and the SCF are the natural place to anchor them.
You'll walk away with a practical map of the overlaps, a shortlist of controls that are designed to help you, and a governance plan that builds resilience, not just something to show auditors.
Cognitive Surrender: Why Your Brain is Giving Up to AI
We use AI every day to write, code, and make decisions. Feels like a productivity win, right? Wharton researchers gave it a name: Cognitive Surrender, taking an answer AI gives you without ever questioning it. In their trials, when the AI was wrong and the person used it anyway, the wrong answer went through nearly 80% of the time. Only one in five people caught it.
As AI mistakes get harder to spot (made-up data, code that looks fine but isn't, hallucinations delivered with total confidence), our own laziness about checking becomes the real problem. If the machine does all the thinking for you, you lose the skill to catch it when it screws up. Research found the damage outlasts the session too, people kept repeating a biased AI's errors after it was gone.
We'll trace what daily AI use is doing to judgment, and lay out what rebuilds the habit. Instead taking the easy way out and using AI less, let's learn how to stay sharp enough to keep control.
Your Encryption Has an Expiry Date: Surviving Q-Day and AI-Speed Attacks
Two clocks are running at once. Q-Day is when quantum computers break today's encryption, and under the EU's roadmap, high-risk use cases come off quantum-vulnerable crypto by 2030. The other clock is AI: attackers run reconnaissance and lateral movement through agents faster than any human team.
These things compound: HNDL (harvest now, decrypt later) means stolen data waits for Q-Day, and AI-speed attacks mean that data was already taken way before most teams noticed.
The session works through the path into a PQC migration, what defending against a machine-speed attacker looks like day to day, and how much crypto-agility the next transition demands.
Seeing Isn't Believing: Deepfakes and the Zero Trust Identity Crisis
Deepfakes are now cheap, fast, and good enough to fool both busy humans and corporate security controls. Voice fraud, executive impersonation, fake "leaks," and AI-generated video approvals for fraudulent wire transfers are no longer theoretical. Real attacks have already bypassed standard Zero Trust defenses by exploiting the one thing the architecture was built on: identity verification.
This session covers how modern synthetic media is made, where it hits hardest, and the solutions that still matter. When an attacker can wear a manager's face on a live call, biometrics and voice authentication stop being controls. We'll walk through what replaces them: cryptographic identity, hardware-bound authentication (FIDO2), C2PA provenance-at-capture, and behavioral verification that current AI cannot trivially fake. At least, not yet.
We'll also cover what the EU AI Act and platform disclosure requirements actually change - and what they don't. You'll leave with a practical checklist for your teams and a clear picture of how Zero Trust needs to evolve to survive the synthetic identity era.
Killing the Paper Tiger: Security That Holds When the Auditor Leaves
Most companies treat security like a checklist: pass the annual audit, buy the tools, file the policy binder, stay one click from a very bad day. That's the Paper Tiger trap. Looks tough on a slide, does nothing when a real attack lands.
Compliance isn't security. An audit tells you a control was documented on the day someone checked, and nothing about the other 364 days, which is where incidents happen.
Closing that gap takes honest risk assessments naming the threats specific to your business, architecture built to take a hit, and day-to-day management that keeps working once the rulebook and reality disagree. You'll walk away with a plan to turn your strategy from a laminated poster into something that actually protects your business, every day.
Automating Humanity: How AI Is Rewiring Work, Judgment and Global Security
The industrial revolution mechanized human muscle. Today, AI is mechanizing human thought, and the training data is the daily output of white-collar workers. Models flatter us, and teams ship code nobody has read.
The same capabilities work for attackers, and we see agents already run large parts of real intrusions today. And that's when the agents don't decide to go rogue themselves. The EU AI Act excludes systems used exclusively for military purposes, and the UN General Assembly has voted on AI's role within autonomous weapons without producing a treaty.
Muscle went first, thought is going now, and judgment is next unless we decide otherwise. You leave with three decisions: where a human stays in the loop, which skills you refuse to outsource, and what you ask of the people writing the rules.
Your AI is Probably Out of Control (And You Know It)
AI governance isn't just an engineering problem anymore - it affects the whole company. Costs spiral, employees use tools you've never approved, and vendors are embedding AI into software you already run. Writing policy is easy; it won't stop a data leak or a model that makes things up. If you want to keep your company safe, you have to move past policy and start using tools that actually watch what the AI is doing.
This session gives you a practical plan to secure how your company uses AI. We cover how to find where AI is hiding in your business and assess those tools for risk; how to track your own AI development so you have an audit trail if something goes wrong; and how to set up guardrails that block a policy violation the moment it happens - without grinding operations to a halt.
Your Next Outage Is Already in Your Supply Chain
In July 2024 a faulty update from one security vendor took down airline check-in, hospital systems and Windows machines around the world. And things only got worse since then. A supplier questionnaire asks how a vendor protects itself - it rarely asks what happens to you when that vendor fails.
This technical session treats the supply chain as a dependency map you can inventory: the software components you ship (SBOM), the cryptography they rely on (CBOM), the models and AI services embedded in tools you already run (AIBOM), and the providers nobody marked as critical.
From that map we find the single points of failure and ask suppliers about post-quantum readiness in a way that produces answers you can verify. We also look at what NIS2 and the Cyber Resilience Act make you answerable for.
You leave with a method for ranking suppliers by how hard they are to replace instead of by spend, and a set of contract questions on PQC readiness and embedded AI.
Compliant, Yet Still Blind to the AI You Run
An audit confirms that an AI policy exists on the day someone checks. It says nothing about what the AI did the other 364 days.
Meanwhile, employees use tools nobody approved, vendors switch on models inside software you already run, and your own teams build AI with no record of what went into it. A policy sees none of that, and the missing record is hard to explain after an incident.
This session treats resilience as the test of AI governance. We put two kinds of evidence side by side: what an auditor accepts (a policy, a register, a training record) and what you need when something goes wrong (an inventory of where AI runs, a log of what it did, a guardrail that blocks a violation as it happens, and a tested way to switch a model off).
We'll then cover how to find the AI you did not buy, how to keep an audit trail for the AI you build or use, and how to run a resilience check for AI governance in order to move from documented to demonstrated.
When the Junior Work Disappears, Who Checks the AI?
Entry-level work is what AI does best, and it is where people used to learn to spot mistakes. First-line alert triage, boilerplate code and draft reports all now go to the machine first.
AI makes you feel faster, even if that's not always the reality. It can also introduce problems at a faster pace than anyone can catch them. A Wharton School paper reports that when an AI gave a wrong answer, people still followed it about 80% of the time.
This becomes a team problem: the SOC and the code review queue both rely on someone who can tell when the machine is wrong, and that skill forms by doing the junior work, a type of work which is the first one getting skipped today.
We look at what happens to skill formation when entry-level tasks go to AI and how a team notices it can no longer verify. You leave with a skills-at-risk table for your own team and a verification routine for AI-assisted work, including what to practice by hand.
DefCamp 2026 Sessionize Event Upcoming
IT Days 2026 Upcoming
Digital Identity - meetup
Women in Tech & Women4Cyber
NDC Security 2026 Sessionize Event
DefCamp 2025 Sessionize Event
NDC Security 2025 Sessionize Event
DefCamp 2024 Sessionize Event
SecureWorld in the era of Artificial Intelligence Sessionize Event
DefCamp Cluj-Napoca Sessionize Event
NDC Security 2024 Sessionize Event
Techorama 2021 Spring Edition Sessionize Event
Global Security and Compliance Community Conference Sessionize Event
EuropeClouds Summit Sessionize Event
Collabdays Lisbon 2020 Sessionize Event
Cloud & Datacenter Conference Germany 2020 Sessionize Event
Experts Live Europe 2019 Sessionize Event
KulenDayz 2019 Sessionize Event
ITCamp 2019 Sessionize Event
Cloud & Datacenter Conference Germany 2019 Sessionize Event
Hyper-V and Hybrid Cloud Community Day Sessionize Event
Experts Live Europe 2018 Sessionize Event
ITCamp 2018 Sessionize Event
Tudor Damian
Cybersecurity, AI & Cloud Advisor @ D3 Cyber
Cluj-Napoca, Romania
Actions
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top