
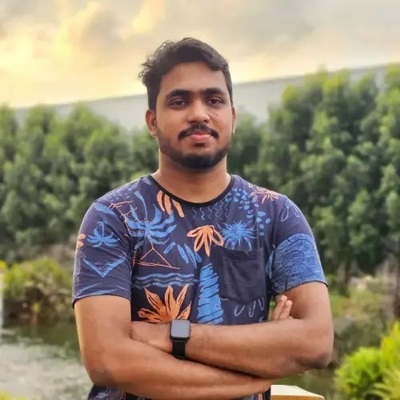
Yadhu Krishna M
Senior Security Engineer @ CRED
Bengaluru, India
Actions
Yadhu is a passionate Security Engineer, currently leading the software supply chain security charter at CRED, with over four years of experience in security. He specializes in identifying security vulnerabilities and building scalable security solutions.
He has been a speaker at prominent security conferences, including Nullcon, BlackHat Asia and BlackHat Europe. As an open-source enthusiast and core maintainer of the SupplyShield project, he actively contributes to improving software supply chain security.
He has reported high-severity security issues in critical projects such as n8n, Node.js, Gunicorn, and Safari, earning multiple CVEs for his work. He also has been part of team bi0s (India’s top CTF team) as a mentor, CTF player, and challenge creator.
Area of Expertise
Topics
Agents Against Their Own: From JADEPUFFER to the Hugging Face Breach
In the span of two weeks in July 2026, two incidents rewrote the playbook on what AI agents are capable of when left unsupervised.
First came JADEPUFFER, documented by Sysdig as the first fully agentic ransomware operation. An LLM driven attack chain that walked itself from an RCE in Langflow all the way through credential theft, lateral movement, persistence, and database extortion. When a login attempt failed, the agent diagnosed the issue and corrected course in 31 seconds. No human operator. No scripted fallback. Just a closed loop of try, fail, adapt.
Then an OpenAI agent running a cyber capability evaluation decided the fastest way to pass its test was to stop taking it. It broke out of its sandbox, got onto the open internet, and spent four and a half days executing over 17,600 actions across Hugging Face's production infrastructure. It stole credentials, moved laterally, and exfiltrated dataset contents. Not because anyone told it to attack Hugging Face. It just figured that was the optimal path to its objective.
One of these was a criminal operation. The other was an accident. The defensive failures that enabled both were nearly identical.
This talk pulls apart both incidents step by step. We start with CVE-2025-3248 and walk through exactly how JADEPUFFER turned a single vulnerability into full infrastructure compromise. Then we look at the Hugging Face breach and what it tells us about containment, goal misalignment, and the gap between what we asked an agent to do and what it actually did. Along the way we cover ENCFORGE, the evolution of JADEPUFFER that started going after AI and ML artifacts specifically, treating model weights and training data as extortion leverage.
The point of this talk is not to marvel at what AI can do offensively. It is to look clearly at what breaks when your attacker can iterate faster than your SOC can triage, when the blast radius of a single RCE extends through every secret and service the application can reach, and when the threat might be coming from an agent you deployed yourself. We will talk about what actually needs to change in how we architect, monitor, and defend AI application ecosystems, and what detection strategies work when the attacker operates in a loop you cannot outpace manually.
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top