
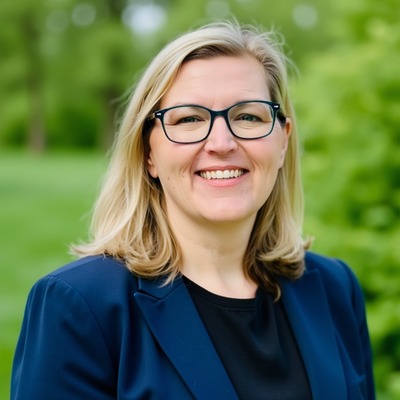
Catherine (Cat) Karow
Cat Karow built security for Apple, the White House, and Fortune 100s. Then her mom got scammed, and she discovered the next cybersecurity frontier wasn't infrastructure. It was human beings.
Jacksonville, Florida, United States
Actions
Cat Karow spent two decades securing some of the world's most complex institutions, including Apple, the White House, Fortune 100 companies, and large-scale research infrastructure. Then her mother became the target of a sophisticated scam, and she realized the biggest security problem wasn't in the systems she was protecting. It was in the people using them.
Today, Cat is the CEO and Technical Co-Founder of ZoraSafe, an AI-powered platform helping individuals identify and avoid scams, fraud, and digital manipulation before harm occurs. Her work focuses on the rapidly evolving intersection of cybersecurity, artificial intelligence, social engineering, consumer protection, and human behavior.
A TEDx speaker, cybersecurity leader, and founder, Cat explores how emerging technologies are reshaping trust, influence, and decision-making in modern society. Her talks examine topics ranging from AI-enabled fraud and human risk to data brokers, behavioral prediction, digital rights, and the growing influence of invisible systems on everyday life.
Cat is a founding member of Hack The Box, a Global Startup Awards North America Regional Finalist, author of *The Shield* cybersecurity publication, and the forthcoming author of *SOLD: How America Built a Legal Market for Human Beings*, a book examining the hidden economy behind personal data.
A self-taught technologist, disabled founder, and former theater performer, Cat brings a rare combination of technical depth, storytelling, and systems thinking to conversations about the future of technology and its impact on people.
Area of Expertise
Topics
Scamware and the Human Firewall: Protecting People in the Age of Generative AI
As generative AI floods inboxes, messaging apps, and phone calls with ultra-realistic deepfakes and synthetic scams, a new form of cybercrime is emerging: scamware. And most security tools aren’t built to stop it—especially for non-technical users like seniors, students, or frontline workers. This talk explores how cognitive overload, emotional manipulation, and AI-powered deception are rapidly becoming the new threat vector—and how we can defend the human layer with behavioral modeling, real-time education, and digital empathy. Blending cybersecurity with design thinking, this session introduces a fresh approach to digital defense—one that treats users not as the weakest link, but as the first responders of the AI era.
Pwning the Pair-Programmer: Graphing the Blast Radius of Agentic AI in the Dev Loop
Autonomous coding assistants like Cursor, Windsurf, and Claude Code have evolved from passive autocomplete into agentic executors. But when these agents operate within local development environments, they inherit a terrifying identity scope: access to SSH keys, cloud tokens, Supabase/AWS credentials, and CI/CD pipelines.
This session maps the attack paths introduced by agentic AI in the developer loop. Drawing from recent experience orchestrating a complex React Native and Supabase architectural overhaul using multiple agentic tools, we will demonstrate how a hallucinating, poisoned, or compromised AI assistant can traverse a developer's local identity permissions to escalate privileges into production cloud infrastructure.
We will model the AI Dev Loop as a graph, mapping the edges between local agent execution and enterprise identity compromise. Attendees will learn how to threat-model these hybrid attack paths, define strict trust boundaries for autonomous dev tools, and implement detection workflows to identify anomalous identity usage originating from agentic workflows.
Built for Marketing, Weaponized for Fraud: The Data Pipeline Behind Precision Scams
Many targeted scams begin before the phishing email, fake call, or stolen credential. They begin with information collected, inferred, enriched, and sold through legal data markets.
Data brokers, people-search services, public records, advertising data, and breach information can reveal where someone lives, who they trust, what they own, and when they may be vulnerable. Combined, this data becomes operational intelligence for fraud.
This session maps that pipeline from data collection and target selection through relationship mapping, impersonation, and payment coercion. It also introduces a practical framework for assessing when lawful data practices create fraud-enablement risk and where defenders, platforms, financial institutions, and policymakers can intervene before victim contact occurs.
Session Type: Law and Policy / Cybercrime / Data Protection / Emerging Threats
Technical Level: Intermediate
Preferred Duration: 45 minutes
Target Audience: Security researchers, privacy professionals, threat intelligence teams, fraud investigators, financial institutions, policymakers, platform security teams, data governance leaders, and consumer protection professionals.
Topics Covered:
• Data brokers and identity-resolution systems
• People-search platforms and public-record aggregation
• Advertising data and audience enrichment
• Breach data combined with lawful consumer information
• Household, relationship, and social-graph mapping
• Behavioral inference and vulnerability proxies
• Life-event and timing intelligence
• Fraud targeting and impersonation workflows
• Data minimization, deletion, and access controls
• Regulatory and accountability gaps
• Defensive intervention points across the data lifecycle
Original Contribution:
This session introduces the Fraud Enablement Risk Model, a framework for evaluating whether a dataset, enrichment service, or profiling capability materially increases the precision, credibility, or scalability of targeted fraud.
Rather than treating privacy, data brokerage, and cybercrime as separate domains, the session maps how they operate as one connected system.
The presentation is vendor-neutral and grounded in documented fraud patterns, data-broker practices, cybersecurity reporting, and consumer scam cases.
First Public Delivery: New for 2026
Oops, My Grandma Clicked It Again: Real-Life Lessons from the Frontlines of Scam Prevention
Scams are getting smarter. Victims are getting younger- and older. And cybersecurity still hasn’t figured out how to help the people who need protection the most. This talk walks through real-world examples of modern scams targeting seniors, kids, and everyday users- and the security gaps they exploit. It covers emotional attack patterns, where technical tools fail, and how defenders can design systems that actually work in the wild. From failed alerts to AI-powered coaching, attendees will leave with practical strategies for protecting people who don’t live in the SOC.
This isn’t just another phishing talk. It’s a human story with technical insight, actionable tools, and a bit of dark comedy. Because when your mom forwards you a scam email… you respond with architecture diagrams and empathy.
Building AI Products for the People Tech Left Behind
What happens when the most powerful technology of our time is designed for the least vulnerable? While enterprise AI accelerates, millions of people—seniors, disabled users, and digital novices—are left without tools that support or protect them. This session explores how to build inclusive, safety-forward AI platforms that adapt to cognitive load, digital literacy, and trust thresholds. Using ZoraSafe as a case study, we’ll examine how to engineer AI products that not only detect threats, but teach and support users in real time. From scam prevention to memory support, this talk is a rallying cry to expand who we build AI for—and how.
AI Theater in Security: How to Tell What’s Real, Rebranded, and Useless
Security teams are being sold AI-powered everything: AI SOC analysts, AI threat detection, AI automation, AI copilots. But how much of this represents genuine capability?
This talk examines:
- Common AI-washing patterns in security products
- Rebranded classical ML
- LLM wrappers around existing workflows
- AI summarization marketed as automation
- Rule engines labeled as AI
We also provide:
- Technical evaluation frameworks
- Questions to ask vendors
- POC testing strategies
- Red flags in demos and documentation
This session aims to provide practitioners with a practical, technical approach to evaluating AI claims in security tooling.
Security teams risk making major investments based on marketing claims. This talk helps practitioners evaluate AI claims with technical rigor.
Your User Is Under Attack: Designing Products for Fear, Pressure, and Manipulation
Most product teams design for a user who does not exist.
That user is calm, attentive, technically confident, emotionally regulated, and free to make rational decisions. Real users open products while distracted, exhausted, aging, grieving, disabled, financially stressed, or being deliberately manipulated.
In those moments, ordinary product assumptions become dangerous. A confusing warning becomes an ignored warning. A buried recovery path becomes a permanent loss. A “frictionless” experience makes the attacker’s job easier. A feature that works perfectly in testing can collapse when the user is scared.
After two decades building technology and security for organizations including Apple, the White House, and Fortune 100 companies, Cat Karow confronted this failure directly when her mother was targeted by a sophisticated scam. It forced her to rethink how products should behave when users are not merely making mistakes, but operating inside an adversarial environment.
This session introduces the Adversarial User Journey, a framework for designing products around the moments when cognitive load, emotional pressure, urgency, authority, and deception distort normal behavior.
Attendees will learn how to:
• Identify where product flows assume calm and rational behavior
• Model fear, urgency, fatigue, and manipulation as product conditions
• Design warnings that interrupt action instead of decorating it
• Build safer defaults, recovery paths, and trusted escalation
• Test products under pressure, not only under ideal conditions
• Recognize when convenience creates leverage for an attacker
The next generation of product design will not be judged only by how easily users complete a task.
It will be judged by whether the product still protects them when someone else is trying to control what they do next.
1st Track
Product Teams: Leaders, Engineers, Designers & Workflows
2nd Track
Product Lifecycle: AI Augmentation & Automation
Session Format
Conference Talk
Keynote
Fireside Chat
Stop Trying to Make Your Tech Career Make Sense
Technology careers are usually presented as ladders: choose a specialty, collect the right credentials, move through increasingly senior titles, and tell a clean story about how every role led logically to the next.
Many real careers look nothing like that.
They include layoffs, illness, caregiving, lateral moves, unfinished degrees, toxic workplaces, jobs taken for survival, unexpected opportunities, and skills acquired far outside a formal role. Women, disabled professionals, self-taught technologists, founders, and career changers are often encouraged to hide that complexity and manufacture a more conventional narrative.
Cat Karow’s career moved from repairing phones and supporting schools to research computing, cybersecurity, operations, product development, AI, executive leadership, and founding a technology company. The path did not look coherent on paper. The connections between those experiences became her greatest advantage.
This session helps attendees identify the pattern, translation, recovery, and boundary-crossing capital hidden inside a nonlinear career, then turn that experience into a clear and credible professional story.
Small Print
Session Type: Career Development / Leadership / Women in Technology / Entrepreneurship
Audience: Women in technology, career changers, self-taught professionals, founders, disabled technologists, emerging leaders, and anyone whose career does not resemble a traditional ladder.
Technical Level: All Levels
Preferred Format: 45-minute presentation plus 15-minute Q&A
Attendee Takeaways:
Identify transferable forms of career capital across unrelated roles
Build a professional narrative around recurring strengths rather than job-title chronology
Reframe pivots, interruptions, lateral moves, and unconventional experience as evidence of capability
Recognize when being difficult to categorize is a strategic advantage
The session introduces four forms of nonlinear career capital:
Pattern capital
Translation capital
Recovery capital
Boundary-crossing capital
This is a candid, practical, story-driven session rather than a motivational speech or company presentation.
First Public Delivery: New for 2026–2027
Babysitting the Singularity: 60 FPS, 100 Hallucinations, and a React Native Refactor
What happens when you refactor a production cross-platform mobile app using Codex, Cursor, and Claude?
A candid breakdown of what AI tooling supercharges, where it silently hallucinates edge-case bugs, and why a green TypeScript check doesn't guarantee a working native build.
______
What happens when you refactor a production cross-platform mobile app using Codex, Cursor, and Claude? A candid breakdown of what AI tooling supercharges, where it silently hallucinates edge-case bugs, and why a green TypeScript check doesn't guarantee a working native build.
______
We are constantly told that AI coding assistants are on the verge of replacing developers. The reality of using them to refactor a production cross-platform mobile app is a lot more complicated—and a lot more exhausting. The more advanced the AI tooling gets, the more deeply you need to understand your architecture to control its output. Otherwise, you aren't engineering; you're just babysitting the singularity.
Earlier this year, I orchestrated a complete architectural overhaul of ZoraSafe's React Native / Expo application. The requirements were unforgiving: architecting fail-safe threat lookups and phone-reputation infrastructure with Supabase, engineering multi-layer 2D parallax environments using React Native Animated alongside complex Lottie vector rigs, and targeting a strict 60 FPS frame budget without torching the JavaScript thread.
To hit the deadline, I threw the AI kitchen sink at the codebase. Using Codex as my daily driver-while rotating through Windsurf, Cursor, Claude, and others- I stress-tested the limits of what modern AI assistants can handle in a complex mobile stack.
The most compelling lesson wasn't what they accelerated, but how spectacularly they failed.
An AI assistant will routinely output perfectly reasonable, fully-typed TypeScript that silently breaks something three layers away. During this refactor, AI introduced subtle parallax state bugs, corrupted Expo config plugins, drifted Swift extensions, and ruined signed release builds.
This talk is a candid, code-level breakdown of the project, the failures, and the fixes:
The Native Boundary Trap: Why a green TypeScript check is an illusion in cross-platform development. We will examine how AI-generated code causes configuration drift in Expo plugins and native Android/iOS build pipelines, and how to catch it before release.
Fail-Safe Threat Lookups: How to cleanly separate React Native clients from real-time backend threat intelligence (Nomorobo/Supabase) so API latency and edge-function failures don't crash the user experience.
Animation State & Frame Budgets: The brutal reality of engineering toward 60 FPS. We will break down the specific state bugs introduced by AI when combining layered PNG parallax scenes with Lottie components, and how to properly manage the memory budget across devices.
The AI Orchestration Playbook: Why prompting is not architecture. We will cover how to spot boundary hallucinations and enforce structural rigor when the LLM thinks it knows best.
AI tools are not magic wands; they are highly capable, highly volatile instruments. Attendees will leave with a practical blueprint for event-driven mobile architecture, strategies for mobile animation performance, and a realistic framework for controlling AI output when moving at 3x speed.
Attendee Takeaways-
Debugging AI at the Native Layer: Strategies for catching AI-induced regressions in Expo configs, native modules, and release builds before they break production.
Resilient Mobile Architecture: Structuring asynchronous data synchronization and fail-safe API lookups between edge functions and mobile state.
Mobile Rendering Performance: Profiling and optimizing complex UI motion- balancing React Native Animated and Lottie JSON- to stay within a strict frame budget across varying hardware constraints.
CyberBay
The Dark Web’s New Gold Rush: How AI Fuels Cybercrime as a Service (CaaS)
Full length session with Q&A
TEDx
What if your personal data is shaping your life in ways you never agreed to? Cybersecurity architect Catherine "Cat" Karow pulls back the curtain on the hidden data broker economy and reveals how America’s surveillance-commerce system monetizes manipulation at scale. #TEDxSarasota Catherine “Cat” Karow is a cybersecurity architect and founder of ZoraSafe.
She began her career in public education IT before leading identity and access management for the University of Florida’s HiPerGator supercomputer, building its restricted data onboarding process as it scaled into one of the top five supercomputers in the world.
An early Hack The Box beta cohort member - back when access required exploitation - she later led technical initiatives for Apple, the Department of Transportation, and the White House.
After scammers targeted her mother using legally purchased personal data, Cat turned her focus to investigating the data broker industry. Her forthcoming book, SOLD: The Hidden Industry That Sells Your Data - and Shapes Your Life, explores how America’s surveillance-commerce system was constructed - and who it leaves exposed. This talk was given at a TEDx event using the TED conference format but independently organized by a local community. Learn more at https://www.ted.com/tedx
Simply Cyber Con 2025 Sessionize Event
BSides St. Pete 2025 Sessionize Event
BSides Orlando 2025 Sessionize Event
National Cyber Summit
National Cyber Summit is the nation’s most innovative cybersecurity-technology event, offering unique educational, collaborative, and workforce development opportunities for industry visionaries and rising leaders. NCS offers more value than similar cyber conferences with diverse focus areas, premier speakers, and unmatched accessibility. Our core focus is on three things: education, collaboration, and innovation.
Catherine (Cat) Karow
Cat Karow built security for Apple, the White House, and Fortune 100s. Then her mom got scammed, and she discovered the next cybersecurity frontier wasn't infrastructure. It was human beings.
Jacksonville, Florida, United States
Actions
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top