
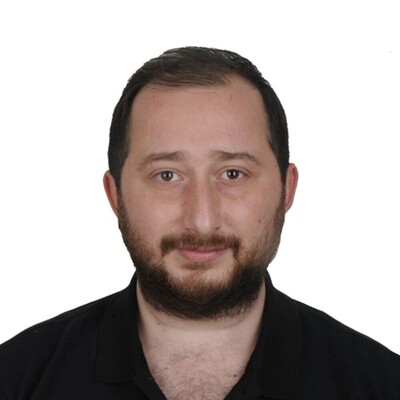
Halil Dursunoglu
Faculty Specialist in Computer Science and Cybersecurity at Western Michigan University, advancing research and education in AI security, secure software engineering, deepfake detection
Kalamazoo, Michigan, United States
Actions
Halil Ibrahim Dursunoglu is a Faculty Specialist in Computer Science and Cybersecurity at Western Michigan University. His work focuses on applied cybersecurity, secure software engineering, secure systems architecture, artificial intelligence security, and deepfake detection. He teaches courses in web application security, network security, secure programming, and cybersecurity-focused systems education while actively mentoring student teams in secure system design, software engineering, and technology innovation.
Prior to academia, Halil held leadership and software engineering roles in industry, including serving as a Chief Technology Officer and Senior Software Engineer, where he led the development of secure software platforms, distributed systems, and enterprise applications. His current research interests include AI security, digital media authenticity, software vulnerability analysis, secure-by-design practices, and cybersecurity workforce development.
Halil serves as a reviewer for IEEE Access, the Journal of Open Source Software (JOSS), and the Journal of Open Research Software (JORS). He has also contributed as a subject matter expert to RSA Conference on AI impersonation threats and deepfake detection. He is a member of IEEE, ACM, and ACM SIGSAC and is committed to advancing cybersecurity education, secure systems research, and the development of the next generation of cybersecurity professionals.
Links
Area of Expertise
Topics
When AI Keeps Rewriting Your Code: Measuring Security Drift in AI-Assisted Software Development
AI coding assistants are rapidly changing how software is built, but their security impact cannot be understood from a single generated response. Development is iterative: developers ask AI to add features, fix bugs, refactor code, and change configurations, creating opportunities for security controls to weaken or disappear.
This talk introduces **security drift**: the gradual introduction, reintroduction, or amplification of vulnerabilities across successive rounds of AI-assisted development. Using experimental examples, I will show how weaknesses involving authentication, input validation, injection, secrets, and insecure configurations evolve as AI repeatedly modifies the same application. Attendees will learn how to measure security drift, identify security regressions, preserve security requirements across prompts, and integrate practical safeguards into AI-assisted development workflows.
When AI Keeps Rewriting Your Code: The Hidden Security Drift Problem
AI coding assistants are changing how software gets built. Developers no longer ask AI to generate code once—they repeatedly ask it to add features, fix bugs, refactor functions, simplify deployment, and solve whatever breaks next. But what happens to security after the tenth, twentieth, or fiftieth prompt?
This talk explores **security drift**: the gradual introduction, reintroduction, or amplification of vulnerabilities as AI-generated software evolves through repeated interactions with coding assistants. A system that begins with reasonable security controls can slowly lose them as individually sensible changes alter authentication, input validation, authorization, secrets management, dependencies, and configuration.
Using experimental results and live examples from iterative AI-assisted development, I will show how vulnerabilities evolve across multiple generations of the same application—and why evaluating a model's security from a single prompt misses an important part of the risk.
Attendees will see how seemingly harmless requests such as “make this easier to deploy,” “fix this error,” or “simplify the authentication code” can create unexpected security consequences. The talk concludes with practical techniques for detecting and limiting security drift, including security invariants, automated analysis, change-aware testing, and human review.
The question is no longer simply whether AI can write secure code. It is whether that code **stays secure when AI keeps rewriting it.**
When AI Keeps Rewriting Your Code: Measuring Security Drift Across Iterative AI Development
AI coding assistants are changing software development from a process of writing code to a continuous conversation: generate an application, add authentication, fix an error, simplify a function, optimize deployment, and repeat. But what happens to security as the same codebase is repeatedly rewritten by AI?
This talk introduces **security drift**: the gradual introduction, reintroduction, or amplification of vulnerabilities across iterative AI-assisted development. Rather than evaluating whether an AI model can generate secure code from a single prompt, this research examines how security changes across multiple revisions of the same application.
Using controlled experiments and automated security analysis, I track vulnerabilities across successive AI-generated code versions and measure when security controls are preserved, weakened, removed, or unintentionally bypassed. The analysis examines issues including authentication, input validation, injection vulnerabilities, secrets exposure, insecure configuration, and security regressions introduced while solving unrelated development tasks.
The talk will demonstrate how seemingly harmless prompts such as “make deployment easier,” “fix this error,” or “simplify the implementation” can alter the security posture of previously generated code. Attendees will see how security drift can be measured, visualized, and detected throughout an AI-assisted development workflow.
The goal is not to argue against AI coding tools, but to show why securing AI-generated software requires continuous security validation rather than a one-time review. Attendees will leave with practical techniques for identifying security drift and integrating security checks into increasingly agentic software development workflows.
Security Drift: How AI-Generated Code Gets More Vulnerable Over Time
AI coding assistants can generate functional software in seconds, but what happens to security when developers repeatedly ask AI to modify, debug, extend, and simplify the same application?
This session explores **security drift**: the gradual introduction, reintroduction, or amplification of vulnerabilities as AI-generated software evolves through iterative prompting. Instead of evaluating AI-generated code from a single prompt, we examine what happens across multiple development cycles. An application may begin relatively secure, but seemingly harmless requests such as “add authentication,” “fix this error,” “make deployment easier,” or “simplify this function” can weaken security controls established in earlier versions.
Through practical examples and experimental results, attendees will see how vulnerabilities involving authentication, input validation, injection, secrets, insecure configurations, and weakened security controls can emerge and evolve across successive AI-generated revisions.
The session will demonstrate methods for measuring and detecting security drift using automated security analysis and security-aware code comparison. Attendees will leave with a practical approach for incorporating AI coding assistants into development workflows without assuming that code that was secure yesterday will remain secure after the next prompt.
Insert Prompt to Opt Out: Reclaiming Security Control from AI-Generated Code
AI coding assistants promise to give developers more control: describe what you want, generate the code, refine it, and ship faster. But what happens when every refinement quietly transfers more security decision-making from the developer to the model?
This talk presents empirical research into security drift in iterative AI-assisted software development: the phenomenon where code that appears to improve functionally across successive AI-generated revisions can simultaneously become less secure. Rather than treating a generated response as a one-time artifact, the research examines the full conversational development process—initial generation, feature requests, debugging, refactoring, and subsequent revisions—to understand how vulnerabilities emerge, disappear, and propagate.
Using the SecureIterate experimental pipeline, I will demonstrate how AI-generated applications can accumulate security weaknesses across iterative development, how seemingly harmless prompts can alter the attack surface, and why developers cannot assume that a previously secure control will survive the next model-generated revision.
The talk will examine vulnerability propagation, security-drift measurement, hallucinated dependencies and software supply-chain exposure, and the limitations of simply asking an AI model to "make the code secure." A live demonstration will show how ordinary feature-oriented prompts can unintentionally transform the security posture of an application without explicitly requesting insecure behavior.
Most importantly, this is not a talk about abandoning AI-assisted development. It is about reclaiming control over it. Attendees will leave with a practical security workflow for treating AI-generated code as untrusted input, measuring security changes between revisions, preserving security requirements across prompts, and introducing automated security gates before generated code reaches production.
In a world where software development is increasingly mediated by AI, opting out does not necessarily mean turning AI off. It can mean refusing to outsource the final security decision.
Halil Dursunoglu
Faculty Specialist in Computer Science and Cybersecurity at Western Michigan University, advancing research and education in AI security, secure software engineering, deepfake detection
Kalamazoo, Michigan, United States
Links
Actions
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top