
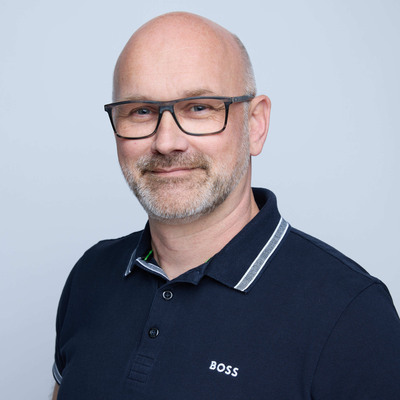
Peter Schmidt
Cloud & Security Architect, Microsoft MVP: M365 & Security, MCSM: Exchange, MCT.
Kolding, Denmark
Actions
Peter is a Cloud & Security Architect based in Denmark with extensive experience in the IT industry, specializing in Messaging, Collaboration, and Cloud security. Since 1996, he has been a consultant, focusing on technologies such as Microsoft 365, Exchange Server, Microsoft Teams, OneDrive for Business, Office 365, Purview Information Protection, and Microsoft Defender Security products.
Peter holds the prestigious Microsoft Certified Solutions Master (MCSM) certification in Exchange and has been recognized as a Microsoft MVP in Microsoft 365. He is a seasoned speaker, having presented at numerous high-profile events, including the European SharePoint Conference, European Collab Summit, Nordic Infrastructure Conference, Workplace Ninja Summit, Microsoft Campus Days, and various local User Group events.
In addition to his professional work, Peter leads the Danish WorkPlace Ninja User Group, which focuses on advancing knowledge in Microsoft Modern Workplace, Productivity, and Security.
Badges


Area of Expertise
Topics
No Phishing Allowed: A Deep Dive into Microsoft Defender for Office and Authtenticated E-mail
Phishing attacks continue to be a major threat to businesses, with attackers using increasingly sophisticated techniques to trick users into revealing sensitive information or infecting their systems with malware.
In this session, you will learn how to implement Microsoft Defender for Office in your organization, and how to use it in conjunction with other anti-phishing strategies. You will also learn how to customize its protection policies to meet the specific needs of your organization, and how to monitor and analyze the reports to understand the threat landscape.
The sessions will provide an overview of best practices for securing your organization against phishing attacks, such as user education, training, and policy development.
After this session, attendees will have a better understanding of how to use Microsoft Defender for Office and other security tools to protect their organizations against email-based threats.
Mastering Email Security using Defender for Office
Phishing attacks present an ever-evolving threat to businesses, employing sophisticated techniques to compromise sensitive information.
This session targets IT and cybersecurity professionals, focusing on deploying Microsoft Defender for Office (MDO) as a pivotal component of your organization’s defense strategy. You’ll gain insights into best practices for configuring MDO to its fullest potential, utilizing AI and machine learning to detect and neutralize phishing attempts before they impact your network.
Covering how to customize MDO’s protection policies to align with your organization's requirements, enhancing security with features like Safe Links, Safe Attachments, Impersonation Protection and the latest features.
Practical demonstrations will guide you in setting up these defenses, monitoring for threats, and analyzing reports to gain a comprehensive view of the phishing landscape.
Beyond technical configurations, this session emphasizes the importance of user education, awareness training as cornerstone practices for securing your organization against phishing attacks.
You will leave this session with best practices and actionable strategies to implement Microsoft Defender for Office and complementary security measures, ensuring robust protection against email-based threats.
Microsoft 365 Copilot - Data Governance
Copilot can only be as safe and as useful as the data it’s allowed to ground on.
In 2026, getting Copilot-ready is no longer just about permissions and tidy SharePoint sites. It’s about governance at scale: understanding where sensitive data lives, reducing oversharing, applying label-driven protection, and enforcing policies consistently across Microsoft 365 and Copilot experiences including Copilot Studio and agents.
In this session, I will cover a practical playbook to make your data discoverable to the right people and inaccessible to everyone else. You’ll see how Microsoft Purview capabilities (classification, sensitivity labels, DLP, retention, audit/eDiscovery) and tools such as DSPM combine with identity controls and collaboration settings can reduce risk without killing productivity.
Mastering Email & Collaboration Security in Microsoft 365 using Defender for Office (2026 Edition)
Most organizations have Defender for Office 365 enabled. Far fewer have it configured in a way that actually reflects how attackers behave or how their users work.
This session is built on real customer environments, not lab setups. We'll walk through the decisions that matter: when preset security policies are the right call, when they're not, and what the gap between "deployed" and "effective" actually looks like in practice.
We'll cover anti-phishing and impersonation protection, Safe Links and Safe Attachments, and the configuration mistakes that quietly create blind spots or generate so much noise that teams start ignoring alerts altogether.
But email is only part of the story. Attackers have figured out that Teams is a trusted channel and most defenses haven't caught up.
We'll look at how Defender extends into Teams to cover malicious links, files, and social engineering that never touches your inbox.
We'll also spend time on Attack Simulator Training not as a box to check, but as a practical tool for reinforcing controls, improving how users report suspicious activity, and closing the gap between detection and response.
You'll leave with concrete configuration guidance, a clearer sense of where the real risks are, and a few things you'll probably want to go fix on Monday morning.
Attendees will leave with:
- A clear understanding of why email authentication is foundational to Defender effectiveness
- Practical Defender for Office 365 configuration guidance for both email and Teams
- Insight into common operational mistakes and how to avoid them
- A realistic approach to combining technical controls with user awareness
From Click to Compromise: What Really Happens After a Phishing Attack
Phishing is no longer just about a user clicking a bad link. In modern Microsoft 365 environments, a single successful phish can lead to token theft, session replay, and full account takeover without triggering traditional alerts.
This session focuses on what actually happens after a phishing attack succeeds, based on real-world incidents and customer environments. We walk through the full attack chain, from the initial user interaction to how attackers leverage tokens, sessions, and trusted identity to move inside the tenant.
You’ll see how Defender for Office 365 processes user-reported phishing, what signals are generated, and where detection can fall short. We’ll trace attacks across mail flow, URLs, identities, and user activity, using the same investigation paths available in real incidents, including Threat Explorer, submissions, and incident queues in the Defender portal.
The session also covers how modern SOC capabilities are evolving. Using Security Copilot and the Phishing Triage Agent, we look at how organizations can reduce noise, prioritize real threats, and improve response quality by automating the analysis of user-reported phishing and enabling faster decision-making.
A key part of the session is understanding identity compromise. From revoking sessions and removing persistence to strengthening policies and improving detection, you’ll leave with practical steps to handle incidents and reduce the likelihood of recurrence.
This session is not theoretical. It is built on real attacks, real mistakes, and the operational reality of responding to phishing in modern Microsoft 365 environments.
A successful phish is often an identity attack, not a mail problem
Modern phishing leads to token theft and session hijacking, allowing attackers to bypass MFA and operate as the user.
Detection depends on signals across multiple workloads
Effective investigation requires correlating email, user reports, Defender alerts, and identity activity to understand what actually happened.
Response speed and quality improve with automation and user reporting
User-reported phishing, combined with tools like the Phishing Triage Agent and automated investigation, helps reduce noise and accelerate incident response.
Microsoft 365 Tenant-to-Tenant Migrations: Critical Decisions and Lessons from the Field
Microsoft 365 tenant-to-tenant migrations are often presented as data migration projects. In reality, moving content is usually the easy part.
The real challenges are identity, coexistence, workload dependencies, security, governance, and ensuring that users can continue to work while accounts, data, and services are transitioning between tenants.
Drawing on real-world migration projects involving mergers, acquisitions, divestitures, and tenant consolidations, this session focuses on the architectural decisions that determine whether a migration becomes a smooth transition or a long list of unexpected problems.
We'll explore identity and coexistence strategies, mail flow design, cross-tenant collaboration, licensing transitions, and workload dependencies across Exchange Online, Teams, SharePoint, OneDrive, and Microsoft Purview. We'll examine where Microsoft's native migration capabilities fit, where third-party tooling can add value, and where neither can solve the underlying business and architectural challenges.
We'll also cover one of the most underestimated parts of any migration: destination readiness. Security controls, governance configurations, permissions, labels, policies, integrations, and compliance settings often require just as much attention as the migration itself.
Throughout the session, I'll share lessons learned from customer migrations, common assumptions that create risk, mistakes that are difficult to reverse, and practical approaches for planning cutover, validation, and user adoption.
Whether you're planning your first tenant-to-tenant migration or your next large-scale consolidation project, you'll leave with practical guidance, real-world lessons learned, and a clearer understanding of the decisions that matter before the first mailbox or document is ever moved.
Your Data Is Not Ready for Copilot. Now What?
Many organizations are eager to roll out Microsoft 365 Copilot, but quickly discover that AI surfaces both the value and the problems hidden within their data.
Oversharing, inconsistent permissions, stale SharePoint sites, external access, missing classifications, sensitive information, and unclear ownership often become visible before organizations are ready to address them. Copilot does not create these governance problems, but it can make the consequences much harder to ignore.
This session focuses on the practical work required to prepare Microsoft 365 for Copilot adoption. Drawing on real-world customer engagements, we’ll explore common governance challenges, how to identify risk areas, and where to focus first to improve security, compliance, and data quality.
We’ll connect SharePoint and OneDrive governance with Microsoft Purview capabilities such as Microsoft Information Protection, sensitivity labels, Data Loss Prevention, and audit. A live demonstration of a custom SharePoint Online governance script will show how to assess a Microsoft 365 environment and turn technical findings into practical governance actions.
Expect a practical session with a live script demo, real-world examples, lessons learned from customer environments, and honest discussions about what to prioritize and what not to do.
Whether you’re preparing for Copilot or already have it in production, you’ll leave with a clearer understanding of how to assess your current data foundation and build a governance approach that supports both security and productivity.
Beyond the Inbox: Building Modern Phishing Protection with Microsoft Defender
Phishing attacks continue to evolve, and email is no longer the only entry point. Attackers combine impersonation, compromised accounts, QR codes, trusted cloud services, collaboration platforms such as Microsoft Teams, and increasingly AI-assisted techniques to bypass traditional defenses and reach users.
This session explores how Microsoft 365 helps defend against modern phishing threats across email and collaboration workloads using Exchange Online Protection, Microsoft Defender for Office 365, email authentication, Safe Links, Safe Attachments, user reporting, and investigation capabilities.
Through live demonstrations, real-world attack scenarios, and lessons learned from customer environments, we'll follow phishing attacks from delivery to detection, response, and recovery. We'll examine how Microsoft protects users in Exchange Online and Microsoft Teams, how attackers attempt to bypass these protections, and what organizations can do to strengthen their defenses.
We'll also look at SPF, DKIM, and DMARC in real-world environments, including where email authentication helps, where it does not, and the common mistakes that can leave organizations exposed.
In addition, we'll discuss emerging phishing trends, including QR-code phishing, AI-assisted attacks, hidden instructions designed to influence AI systems, and why layered protection remains essential as attackers continue to evolve their techniques.
Whether you're responsible for messaging, collaboration, security, or Microsoft 365 administration, you'll leave with practical guidance and a clearer understanding of how to build layered phishing protection across Microsoft 365.
From Classification to Enforcement: Building Effective DLP in Microsoft 365
Many organizations implement Data Loss Prevention and quickly discover that the technology is rarely the hardest part. The real challenge is understanding your data, classifying it correctly, and implementing protection that supports both security and productivity.
In this session, we'll take a practical look at how organizations use Microsoft Purview to discover, classify, protect, and govern sensitive information across Microsoft 365. Through live demos, practical examples, and lessons learned from customer environments, we'll explore how Information Protection, Sensitivity Labels, Data Loss Prevention, and Endpoint DLP work together to reduce data exposure and support modern compliance and security requirements.
We'll discuss common implementation challenges, policy design, rollout strategies, user adoption, and the mistakes that often create friction for both users and administrators. We'll also look at how to move from initial classification to effective enforcement and ongoing governance.
Whether you're starting your Microsoft Purview journey or improving an existing deployment, you'll leave with practical guidance and a better understanding of how to make DLP and data protection work in the real world.
Microsoft Purview in Practice: Where to Start and What to Prioritize
Microsoft Purview offers a wide range of capabilities for protecting, governing, and managing information, but knowing where to start is often the biggest challenge. Should you begin with Sensitivity Labels, Data Loss Prevention, Retention, Audit, eDiscovery, Insider Risk, or something else entirely?
In this session, we'll take a practical look at different Microsoft Purview deployment journeys and discuss how organizations can prioritize the capabilities that deliver the most value based on their business requirements, regulatory obligations, and data risks.
Drawing on lessons learned from real-world deployments, we'll explore common starting points, proven implementation approaches, and the mistakes that often make Purview projects more complicated than they need to be. We'll cover capabilities such as Information Protection, Sensitivity Labels, Data Loss Prevention, Retention, Audit, eDiscovery, and Insider Risk, but more importantly, we'll discuss when and why to implement them.
We'll also look at something that is often overlooked in Purview projects: the technical implementation is usually the easy part. Understanding how information is used, educating users, building awareness, and investing in communication, training, and adoption are often far more important to long-term success than the technology itself.
Whether you're planning your first Purview deployment or looking to refine an existing strategy, you'll leave with practical guidance, lessons learned from the field, and a framework for building a Purview roadmap that fits your organization rather than simply following a best-practice checklist.
From Click to Compromise: Investigating Modern Phishing Attacks in Microsoft 365
Phishing attacks have changed. Today's attacks are no longer limited to fake emails and stolen passwords. Attackers use AI to generate highly convincing lures, exploit trusted platforms, steal tokens and sessions, and turn a single successful phish into a full identity compromise.
In this session, we'll follow a real-world phishing incident from the first user interaction through investigation, containment, and recovery. Using lessons learned from customer environments, we'll explore what actually happens after an attacker gains access and how security teams can uncover the full scope of an incident.
We'll trace the attack path across Microsoft 365, following the evidence through email, identities, user activity, and security signals. Along the way, we'll look at how Microsoft Defender, Exchange Online, Entra ID, user reporting, and modern investigation workflows can help defenders understand what happened and respond effectively.
You'll see where traditional assumptions about phishing often break down, why a successful phish is frequently an identity attack rather than an email problem, and how attackers are increasingly leveraging AI-generated content, trusted services, and evolving social engineering techniques to bypass defenses.
We'll also discuss practical response and recovery strategies, including how to identify compromise, contain attackers, reduce persistence, and strengthen defenses to prevent similar incidents in the future.
Whether you're responsible for messaging, identity, security operations, or Microsoft 365 administration, you'll leave with practical guidance, real-world lessons learned, and a better understanding of what modern phishing attacks look like beyond the inbox.
Key Takeaways
Understand how modern phishing attacks evolve from email delivery into identity compromise and account takeover
Learn practical investigation techniques across Microsoft 365, Defender, and Entra ID
Recognize common attacker tactics involving token theft, session hijacking, and AI-enhanced phishing campaigns
Gain actionable response and recovery guidance based on real-world incidents and lessons learned
Microsoft Zero To Hero Community - 2025 User group Sessionize Event Upcoming
ELDK27 - Experts Live Denmark Sessionize Event Upcoming
Experts Live Denmark 2026 Sessionize Event
Workplace Ninja Summit 2025 Sessionize Event
aMP Hammamet 2025 Sessionize Event
India Cloud Security Summit 2025 Sessionize Event
European M365 Summit 24.-25. Juni 2025 Sessionize Event
Experts Live Denmark 2025 Sessionize Event
Festive Tech Calendar 2024 Sessionize Event
NIC Empower 2024 Sessionize Event
AI Day 2024
Delivered a Copilot session
Workplace NInja User Group Denmark
Delivered a session about Microsoft 365 backup.
6th Cloud8 virtual Summit 2024 Sessionize Event
Festive Tech Calendar 2023 Sessionize Event
ESPC23 - European SharePoint, Office 365 & Azure Conference Sessionize Event
AI Day 2024
Delivered a Copilot session.
NIC Cloud Connect 2023 Sessionize Event
Experts Live User Group Denmark
Workplace Ninja Summit 2023 Sessionize Event
Workplace Ninja Summit 2023
Delivered two sessions about E-mail Security and Secure Score.
5th cloud8 virtual Summit 2022 Sessionize Event
NIC X Edition Sessionize Event
Microsoft 365 Virtual Marathon 2022 Sessionize Event
Nordic Virtual Summit 3rd Edition Sessionize Event
M365 Below in Chicago! Sessionize Event
Nordic Virtual Summit Second Edition Sessionize Event
ExpertsLive Norway 2021 Sessionize Event
Nordic Virtual Summit Sessionize Event
2nd cloud8 virtual Summit in 2020 Sessionize Event
Nordic Infrastructure Conference 2020
Nordic Infrastructure Conference 2020
Delivered two sessions about Teams and Security.
Microsoft Tech Summit Stockholm 2018
Proctor on a workshop about Microsoft Teamwork (Teams, Groups, OneDrive, Yammer).
Nordic Infrastructure Conference 2017
Delivered two sessions, one about OneDrive for Business and one about Exchange Online (Office 365).
Nordic Infrastructure Conference 2016
Delivered two sessions about Office 365 and Exchange.
Nordic Infrastructure Conference 2015
Delivered two sessions about Exchange and Office 365.
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top