
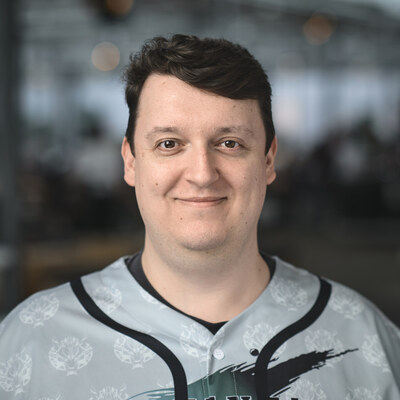
Wesley Cabus
Customer Success Engineer at Duende Software. Coffee Enthusiast.
Antwerpen, Belgium
Actions
Wesley is a Customer Success Engineer at Duende Software, helping Duende's customers to be successful by assisting developers with issues, documenting common problems and teaching about security / identity.
He's also a Microsoft MVP, board member of the VISUG meetup in Belgium and speaker at meetups and conferences, such as NDC Copenhagen, London and Sydney, ConFoo Montreal, WeAreDevelopers Berlin, Update Conference, TechDays, Swetugg, DevConf, DeveloperDays and Techorama.
Links
Badges


Area of Expertise
Topics
ASP.NET Core, from DEV to PRD
Your ASP.NET Core web app runs fine on your machine and even in the DEV environment. But what happens when you deploy to multiple instances behind a load balancer? Suddenly, things that looked solid in DEV start breaking in PRD 😨
In this session, I'll show some common pitfalls you may encounter when deploying your apps to production:
* Data protection configuration that works on multiple instances
* Distributed vs in-memory caching
* Load balancer or reverse proxy - which headers to forward?
* Ready, live and health checks
Come for the horror stories, leave with practical fixes!
ASP.NET Core Authentication Explained
Ever had to add the ability to your ASP.NET Core web application to authenticate users? Or build an API that needs to verify it's being called by the right clients? Be honest: did you fully understand what you were doing, or did you just copy-paste some code from StackOverflow or your favorite AI assistant and hope for the best?
In this session, I'll explain how authentication actually works in ASP.NET Core from start to finish. We'll begin with configuring the middleware, explore how authentication schemes are selected, and dig into handlers, tokens, cookies and headers.
Bring your questions, and leave your fear of AddAuthentication() behind!
Are you sure your access tokens are really secure?
You've read about OAuth 2.0 and decided to secure your web API using JWT access tokens. To implement this, you're likely relying on an open-source library to parse and validate these tokens, confident that your configuration will only accept tokens from your trusted issuer or token service.
But here's the real question: are you absolutely certain that your API only accepts access tokens issued by your service?
In this session, I’ll demonstrate some tricks that can bypass improperly configured token validation. You’ll see how easy it is to fool your API if you’re not careful. But don’t worry, I’ll also show how to write tests that ensure your application is protected against these exploits, keeping your data and users safe.
Emulating a Game Boy in .NET
In 1989, Nintendo released their first handheld console with cartridges, the Game Boy, which sold over 100 million of units. This device has been the inspiration for game developers around the world to start creating games, and even today, games are still being created for the Game Boy, although not officially on cartridges.
Enter the world of emulation, where the Game Boy is now available as a .NET project, even running using WebAssembly! Want to know more about how to emulate a CPU, graphical unit, hardware interrupts and more? Let's dive into C# code and dusty hardware manuals on this journey back to our favorite Italian plumber.
Learning Objective 1:
Learn how to emulate old hardware using C#
Learning Objective 2:
Using WebAssembly's new multithreaded capabilities to deliver high-performant WASM libraries
Learning Objective 3:
Bonus: see first-hand how a fun side project like this can make you a better developer
Protect, Unprotect, Regret? Using ASP.NET Core Data Protection for Sensitive Data
Every ASP.NET Core app already depends on the Data Protection API: it's what encrypts and tamper-proofs your authentication cookies and anti-forgery tokens without you needing to think about it.
So when your application has other sensitive data to protect, like PII information or stored secrets, using the same built-in stack feels like the right choice to make. However, it can also become a quiet path to data loss if you don't understand what the API was designed for.
This session is a practical tour of using Data Protection for real application data. We start with the fundamentals, showing:
- how IDataProtectionProvider, CreateProtector and Protect/Unprotect works
- how to derive protectors from each other and why this matters
- how to create time-limited or self-expiring payloads using ITimeLimitedDataProtector
Without a proper configuration, losing a key ring means your protected data is gone forever, turning "Protect" into "Regret." We’ll conclude by covering the exact Data Protection configurations needed to keep your keys safe and your data secure.
Killing Session Theft: Device Bound Session Credentials Explained
Infostealer malware doesn't need your password if it can steal your authentication cookie from disk or memory, and replay it on another machine. Any webserver happily accepts the stolen cookie since it was issued by the webserver itself. This type of attack bypasses WebAuthn or MFA entirely, since the cookie gets stolen *after* you have authenticated. Since there's no real fix against this, we can only issue cookies with a shorter lifetime to minimize the attack window. Until now.
Device Bound Session Credentials (DBSC) is a W3C draft introducing a solution, by tying the session cookie to the browser or device. The browser generates a private/public key pair, storing the private key ideally in secure storage like a TPM, while the webserver only issues short-lived authentication cookies. When the cookie expires, the browser can then only refresh the cookie by signing a server-issued challenge using that private device-specific key. While this doesn't prevent cookie and session theft, it does minimize the risk since cookies go stale faster and cannot be renewed without the device's private key.
During this session, I'll demonstrate how DBSC architecturally works, including an example implementation in ASP.NET Core with .NET 11 using the experimental Microsoft.AspNetCore.Authentication.DeviceBoundSessions NuGet package. And to prove it works, I'll perform a live attack: after stealing a valid session cookie, we'll see exactly when the stolen cookie stops working because the refresh operation can't be signed.
Identity & Access Control for modern Applications and APIs using ASP.NET 10
Duende Software's legendary training on Identity and Access Management was originally created by Dominick Baier and Brock Allen. With their world-class knowledge, they’ve created a workshop focused on the essential concepts and how they interact. Based on the experience from decades of consulting for hundreds of customers, the workshop is packed with content relevant for real-world modern systems.
Modern application design is more complex than it was a decade or two ago. A modern application is expected to be mobile-first and cloud-based. Microsoft’s answer to these demands was to create ASP.NET Core. A decade later, ASP.NET Core has matured into a trusted development platform covering all components needed in a modern application architecture.
Multi-platform, microservices, multi-client, and highly-mobile users bring a set of challenges that were not present a decade ago. A modern application cannot be secured just by handling access control in the single UI of the application, because there is no longer any single UI. There are web applications, mobile apps and APIs that are exposed to partners and third-party developers. Internally, an application often consists of multiple microservices calling each other. These services are also frequently reused between different applications and externally visible APIs.
To properly secure this landscape, a zero-trust approach is required. There should be a verifiable proof of the end user (or end machine) identity for any user session established or API.
This workshop is your chance to dive into all these security-related technologies. Learn how to securely connect native and browser-based applications to your back-ends and integrate them with enterprise identity management systems as well as social identity providers and services.
After attending this workshop you will have a good understanding of the concepts and will be ready to start implementing a modern identity and access management solution tailored to your organization’s needs.
You will learn:
- The ASP.NET Core Authentication and Authorization System Design Principles.
- How to use external authentication and offer single sign-on and single logout.
- How to securely call APIs on behalf of the authenticated user.
- The principles of the OpenID Connect and OAuth 2.0 Protocols.
- An overview on how to configure, customize, and deploy Duende IdentityServer.
Day 1: Authentication
- ASP.NET Core Fundamentals
- Claims
- Authentication
- Cookie-Based Sessions
- Data Protection
- Authorization
- Tokens
- External Authentication in ASP.NET Core
- Identities and Identifiers
- Account and Identity Linking
- External Login Callback Pattern
Day 2: OpenID Connect (OIDC) & OAuth 2.0
- OpenID Connect
- Clients
- Scopes
- Web Application Patterns
- Single Sign On / Single Sign Off
- Federation Gateway
- Home Realm Discovery
- Protecting APIs with OAuth 2.0
- Machine-to-Machine
- Interactive Applications
- Authorization Code Flow
- Proof Key Code Exchange
- Token Lifetime Management & Refresh Tokens
- Client Application Types
- Server-Side Web Apps
- Single Page Applications
- Backend-for-Frontend (BFF) Pattern
- Mobile/Native Apps
Computer Setup:
Attendees will need to bring a computer with the latest .NET Core SDK and the IDE of their choice (e.g. Visual Studio) installed.
CloudBrew 2026 - A two-day Microsoft Azure event Sessionize Event Upcoming
Techorama 2026 Netherlands Sessionize Event Upcoming
.NET Day Switzerland 2026 Sessionize Event
DevSum 2026 Sessionize Event
Techorama 2026 Belgium Sessionize Event
CloudBrew 2025 - A two-day Microsoft Azure event Sessionize Event
Update Conference Prague 2025 Sessionize Event
NDC Copenhagen Developers Festival 2025 Sessionize Event
Swetugg Stockholm 2025 Sessionize Event
VisugXL 2024 Sessionize Event
Update Conference Prague 2024 Sessionize Event
DevConf 2024 Sessionize Event
Copenhagen Developers Festival 2024 Sessionize Event
dotnetdays 2024 Sessionize Event
Visug User group Sessionize Event
NDC Sydney 2024 Sessionize Event
CloudBrew 2023 - A two-day Microsoft Azure event Sessionize Event
.NET Developer Conference '23 Sessionize Event
Update Conference Prague 2023 Sessionize Event
Swetugg Gothenburg 2023 Sessionize Event
WeAreDevelopers World Congress 2023 Sessionize Event
Developer Week '23 Sessionize Event
NDC London 2023 Sessionize Event
VisugXL 2022 Sessionize Event
.NET DeveloperDays 2022 Sessionize Event
Techorama Netherlands 2022 Sessionize Event
Techorama 2022 BE Sessionize Event
DevSum 2022 Sessionize Event
VisugXL 2021 Sessionize Event
VISUG Sessionize Event
Build Stuff 2020 Lithuania Sessionize Event
NDC Sydney 2019 Sessionize Event
Microsoft Techdays 2019 Sessionize Event
Wesley Cabus
Customer Success Engineer at Duende Software. Coffee Enthusiast.
Antwerpen, Belgium
Links
Actions
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top