
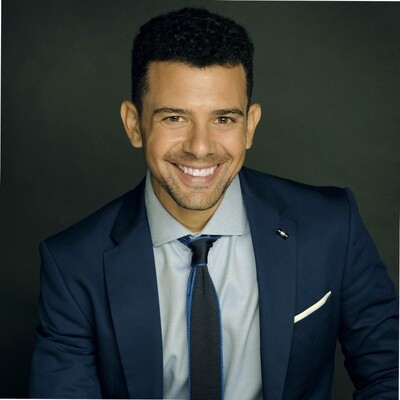
Jorge Litvin
Founder & CEO | Safe-U
Founder & CEO | Safe-U
Buenos Aires, Argentina
Actions
Jorge Litvin is a criminal lawyer turned cybersecurity strategist — author, international speaker, university professor, Founder & CEO of Safe-U, and board advisor.
He works at the intersection of cybersecurity, business risk, AI and organizational culture, translating technical complexity into decisions that executives and boards can act on.
Author of Hackeados (200,000+ downloads across 35 countries), he has spoken at more than 300 events in 10+ countries and 30 universities across 15+ countries, in Spanish and English.
As a regional media reference, he reaches 100,000+ professionals across social media and publishes columns in FORBES, Infobae, La Nación, El País, and CNN, among others.
His thesis: cybersecurity needs judgment, not fear.
Jorge Litvin es abogado penalista especializado en cibercrimen devenido en estratega de ciberseguridad — autor, conferencista internacional, profesor universitario, Founder & CEO de Safe-U y asesor de directorios.
Trabaja en la intersección de la ciberseguridad, la gestión de riesgos, la IA y la cultura organizacional, traduciendo complejidad técnica en decisiones que ejecutivos y directorios pueden tomar.
Autor de Hackeados (200.000+ descargas en 35 países), ha expuesto en más de 300 eventos en 10+ países y 30 universidades en 15+ países, en español e inglés.
Como referente regional de medios, llega a más de 100.000 profesionales en redes sociales y publica columnas en FORBES, Infobae, La Nación, El País, CNN y otros medios.
Su tesis: la ciberseguridad necesita criterio, no miedo.
Links
Area of Expertise
Topics
The Spiral of Change: A Methodical Approach to Shaping Human Behavior en
Cybersecurity awareness isn’t just about phishing simulations and annual trainings—it’s about transforming behavior. The Spiral of Change is a 10-step framework designed to reshape how organizations embed security into their culture. Instead of isolated campaigns, this approach creates a continuous cycle of diagnosing gaps, engaging stakeholders, empowering employees, and adapting to new threats. In this talk, we’ll break down practical strategies to move from “checking the box” training to real cultural transformation. Attendees will walk away with a clear roadmap and actionable tools to make security awareness stick, no matter the size or type of organization. If you’ve ever felt your awareness program isn’t working—this session will show you how to fix it.
Hacking culture en
In this session, we'll elevate the discussion around the human factor in cybersecurity, highlighting its role as the broadest attack surface yet often the most neglected. I'll argue that the onus is on organizations, not individuals, to elevate their security posture through education and training, aligned with existing regulations and frameworks that mandate user training. By introducing a proprietary framework, which has been applied across hundreds of clients with measurable success, I aim to shift the narrative from mere awareness to fostering a profound and lasting cybersecurity culture change. Attendees will gain practical insights and tools, ready to be implemented, to transform their approach to human-centric cybersecurity, ensuring a more resilient organizational defense.
Pitching cybersecurity: Frame it Their Way, Secure it Your Way en es
In today’s high-stakes cybersecurity environment, communicating the value of security initiatives to non-technical executives is crucial. This session tackles the communication gap between cybersecurity professionals and business leaders, with practical strategies to help executives understand, support and endorse your projects.
At its core is the Security Enabler Canvas, a tool I designed to translate technical cybersecurity challenges into strategic business conversations with the C-suite.
Attendees will learn to:
Understand what executives and board members expect when they receive a cybersecurity proposal, and tailor the pitch accordingly.
Map and present a project in business language, using frameworks such as the Business Model Canvas.
Align cybersecurity objectives with broader business goals, so the project resonates with executive priorities.
Target audience: cybersecurity leaders (CISOs, CIOs, heads of cybersecurity, cybersecurity managers) and professionals who present projects to executives.
Duration: 45–60 minutes. A 2-hour hands-on version (Learning Lab) is also available.
Language: Spanish or English.
Delivered at: ISC2 Security Congress 2024 (rated 4.8/5 by attendees), ISACA Uruguay, Ekoparty 2025.
Technical requirements: standard projector and audio.
Beyond the Perimeter: Building Omnichannel Security Awareness for Third Parties en es
When we think about “security awareness,” most companies look inward—training employees to avoid phishing and social engineering. But what about the risks that live outside your walls?
In industries like banking, fintech, crypto, and insurance, regulators demand that awareness also reaches customers, partners, and even suppliers.
In this session, we’ll explore how to design omnichannel awareness campaigns that actually work: using social media, in-app alerts, influencers, branch posters, and more.
You’ll see how to adapt the same core message to multiple audiences, measure whether it sticks, and integrate external and internal campaigns into a single security story. If you want to transform your entire ecosystem into proactive allies against cyber threats—not just your employees—this talk will give you the blueprint.
Target audience: security awareness, security, GRC, marketing and communications leads in regulated industries (banking, fintech, crypto, insurance).
Preferred duration: 30 to 45 minutes.
Language: Spanish or English.
Series B(reach): How Startups can Leverage Cybersecurity for Growth en es
Startups thrive on speed, but that same speed makes them prime targets. Attackers know early-stage companies are often under-defended, while enterprise buyers and investors now expect rigorous cybersecurity due diligence before signing contracts or writing checks.
This session is aimed at CTOs and CISOs in high-growth startups. It traces the path from ideation to IPO, showing how security maturity must evolve alongside business growth. Attendees will learn:
The top cyber risks that disproportionately hit startups.
The security checkpoints that customers and investors require at each funding stage.
How to turn cybersecurity from a compliance burden into a sales accelerator and valuation booster.
Grounded in real breaches, hard data, and pragmatic roadmaps, this talk reframes security as the difference between scaling successfully—or stalling at “Series B(reach).”
Target audience: Founders, CTOs and CISOs of high-growth startups.
Level: intermediate.
Duration: 45 minutes.
Language: Spanish or English.
Technical requirements: standard projector and audio.
GPT-Crime: Cybercrime and Cybersecurity Powered by AI en es
Artificial intelligence is no longer a future trend — it’s a present force reshaping both cybercrime and cybersecurity. This session begins by exposing how criminals are already leveraging AI tools to scale and sharpen their attacks: from automated phishing and deepfakes to adaptive malware and targeted exploitation of AI model vulnerabilities. Through real-world examples, we’ll uncover how these tools are transforming the threat landscape and raising the stakes for defenders.
Then, we’ll shift focus to the other side of the equation: specific, real-life use cases where AI is becoming a powerful ally for cybersecurity teams. From real-time threat detection and incident response automation to intelligent risk prioritization and enhanced resilience strategies, we’ll explore how organizations are already integrating AI into their security operations.
The session will close with a critical reflection: AI is not inherently good or bad — its impact depends on how we choose to use it. In a world where speed and scale define both attacks and defenses, ethical and strategic adoption of AI will be key to staying ahead.
Key Takeaways:
Understand how cybercriminals are exploiting AI to automate and scale attacks.
Discover specific, real-world use cases of AI applied to cybersecurity.
Learn practical strategies to defend against AI-powered threats.
Target audience: security, IT, risk and GRC professionals, and leaders who need to understand how AI is changing both cybercrime and defense. General level.
Preferred duration: 60 mins.
Language: Spanish or English.
Technical requirements: standard projector and audio.
Hackers Are From Mars and Executives Are From Venus en es
Budgets that never get approved, incidents where everyone looks for someone to blame, projects that security learns about only after something goes wrong—these are not technical failures; they are communication failures.
In this session, we’ll explore the cultural and linguistic gap between cybersecurity teams and executives—why they think differently, speak differently, and often misunderstand each other.
Through real-world examples and years of boardroom experience, I’ll show how to decode the language of the business and translate technical risks into strategic priorities.
You’ll learn how to frame cybersecurity conversations that resonate with leaders, build credibility, and turn “no” into “how soon can we start?” Because earning a seat at the table isn’t about being louder—it’s about being understood.
Target audience: cybersecurity leaders (CISOs, CIOs, heads of cybersecurity, cybersecurity managers).
Estimated duration: 45–60 minutes.
Language: Spanish or English.
Technical requirements: standard projector and audio.
Traffic lights don’t prevent collisions: how to move from colors to decisions. en
For years, cybersecurity has been expected to “prevent attacks.” That expectation is common—and flawed. Incidents can happen even with strong controls. The real problem is making decisions blindly.
This session introduces a shift in mindset: risk management is not about implementing controls or turning “red” into “yellow.” It is about making informed decisions on which scenarios to accept, mitigate, transfer, or avoid—based on risk appetite, priorities, and constraints.
We start by clarifying a widespread confusion: what risk is (and what it is not), separating it from threats, vulnerabilities, findings, controls, or maturity. Then we examine why qualitative methods (risk matrices and heat maps) are weak decision inputs: ambiguity, bias, low repeatability, and poor comparability—especially when you need to choose between “high vs. high” risks or build a cost-benefit case.
Finally, we introduce quantification as the natural evolution of risk management, showing how FAIR translates cyber scenarios into business terms the organization can understand and act on: loss event frequency/probability, loss magnitude, and ranges. We close with practical use cases: control and roadmap prioritization, budget justification, risk appetite discussions, board/finance communication, and third-party and cloud risk evaluation.
Target audiencie: CISOs, security leaders, GRC/Compliance teams, risk managers, auditors, IT leaders, finance stakeholders, and executives involved in prioritization and risk acceptance.
Estimated duration: 35-45 mins
The Governance Retrofit: Shape the Culture, Before It Shapes the Risk en es
The CEO walked in and said: "Everyone uses AI now." The room applauded. No one asked the hard questions.
No policy. No inventory. No defined expectations. No answer to what "using AI" actually means — what data can flow where, which tools are approved, or what happens when something goes wrong. Just a mandate. And a cultural vacuum the organization filled on its own terms.
This is how Shadow AI begins. Not with malice. With obedience.
People did exactly what they were told. They used AI — all of it. Personal accounts carrying corporate data. Unauthorized integrations. Ungoverned agents with unrestricted access to sensitive systems. They optimized for the only clear objective they had. IBM's 2025 research puts the cost at an additional $670K per breach — not from external attacks, but from behavior no one governed.
Then security arrived with controls. And security became the enemy.
Not because the controls were wrong. They were necessary. But they arrived after the culture did. Every restriction became an obstacle to what leadership explicitly asked for. The security team wasn't fighting a threat — it was fighting the CEO's own mandate. Employees learned to route around it, because their goal was clear and the controls were just friction.
Most organizations in this room already have this problem. This session isn't about building AI governance from day zero. It's about retrofitting governance into a culture that already has its own rules — and winning anyway.
The Governance Retrofit is a four-layer framework for organizations that need to govern AI culture from where they are:
Inventory first. You can't govern what you don't know exists. An AI inventory isn't bureaucracy — it's your actual risk surface.
Policy as communication, not compliance. The first governance document has to speak the language of the business. A legal memo nobody reads isn't governance — it's theater.
Culture before controls. Controls slow down wrong behavior. Culture installs right behavior. Deploy them in the wrong order and you're not governing — you're negotiating against yourself.
Measure what's observable. Not policies signed. Not training hours logged. Actual behavior: what tools, what data, what accounts.
Attendees will leave with a governance sequence they can implement from day one — and the language to make the case to the leadership that started this problem in the first place.
Target audience: CISOs, CIOs, risk and GRC leads, and AI governance leaders.
Level: intermediate. Format: keynote.
Duration: 45-60 mins
Language: Spanish or English.
Technical requirements: standard projector and audio.
Black Box Risk, White Box Decisions en es
Most organizations manage risk like a black box: a register with hundreds of items, scores and traffic lights that no one can quite explain. Yet decisions get made on top of it: accept, avoid, transfer or mitigate.
The trouble starts the moment someone opens the box. The CFO asks what the budget is based on. The auditor questions a missing control. A customer challenges an answer during due diligence. The insurer has to put a price on the risk. Or, after an incident, someone asks what was known, how the risk was assessed, and why you decided what you did.
This talk starts with why heat maps fail as a basis for decisions, then introduces FAIR (Factor Analysis of Information Risk) from the technical side: risk as a scenario (asset, threat, effect), loss frequency and magnitude estimated as ranges instead of single numbers, and the simulation that turns those ranges into an annual loss distribution. Every assumption is visible, dated, and carries its uncertainty.
We then walk through real, anonymized cases: how FAIR-based quantification changed a specific decision, which data and assumptions supported it, and how it held up when challenged.
You will leave with a practical test to tell a risk decision you can explain and defend from one you can only argue about.
Risk can be a black box. Your decision can’t.
El problema aparece cuando alguien quiere abrirla: el CFO que pregunta en qué se sostiene un presupuesto, el auditor que cuestiona la ausencia de un control, el cliente que pone en duda una respuesta durante una due diligence, la aseguradora que tiene que ponerle precio al riesgo, o quien después de un incidente pregunta qué se sabía, cómo se había evaluado ese riesgo y por qué se decidió como se decidió.
La charla empieza por qué los mapas de calor no alcanzan como insumo de decisión y presenta FAIR (Factor Analysis of Information Risk) desde lo técnico: el riesgo como escenario (activo, amenaza, efecto), la estimación de frecuencia y magnitud de pérdida con rangos en lugar de puntos, y la simulación que convierte esos rangos en una distribución de pérdida anual. Los supuestos quedan a la vista, con fecha y con su incertidumbre.
Luego se aplica a casos reales anonimizados: cómo la cuantificación basada en FAIR cambió una decisión concreta, qué datos y supuestos la sostuvieron, y cómo se defendió ante quien la cuestionó.
Quienes asistan se llevarán un criterio práctico para distinguir una decisión de riesgo que puede explicarse y defenderse de una que simplemente puede discutirse.
El riesgo puede ser una caja negra. La decisión no.
Based on anonymized real cases. Vendor-neutral, no product content.
Target audience: CISOs, risk and GRC leads, internal auditors and security leaders who have to defend budgets and decisions to executives, auditors or insurers.
Preferred duration: 40 minutes (30–35 talk, 5–10 Q&A). Session language: Spanish or English.
Technical requirements: standard projector and audio.
Black Box Risk, White Box Decisions en es
Casi todas las organizaciones gestionan el riesgo como una caja negra: un registro de cientos de ítems, scores y semáforos que nadie sabe exactamente cómo se calcularon. Y sobre esa caja se toman decisiones: aceptar, evitar, transferir o mitigar.
El problema aparece cuando alguien quiere abrirla: el CFO que pregunta en qué se sostiene un presupuesto, el auditor que cuestiona la ausencia de un control, el cliente que pone en duda una respuesta durante una due diligence, la aseguradora que tiene que ponerle precio al riesgo, o quien después de un incidente pregunta qué se sabía, cómo se había evaluado ese riesgo y por qué se decidió como se decidió.
La charla empieza por qué los mapas de calor no alcanzan como insumo de decisión y presenta FAIR (Factor Analysis of Information Risk) desde lo técnico: el riesgo como escenario (activo, amenaza, efecto), la estimación de frecuencia y magnitud de pérdida con rangos en lugar de puntos, y la simulación que convierte esos rangos en una distribución de pérdida anual. Los supuestos quedan a la vista, con fecha y con su incertidumbre.
Luego se aplica a casos reales anonimizados: cómo la cuantificación basada en FAIR cambió una decisión concreta, qué datos y supuestos la sostuvieron, y cómo se defendió ante quien la cuestionó.
Quienes asistan se llevarán un criterio práctico para distinguir una decisión de riesgo que puede explicarse y defenderse de una que simplemente puede discutirse.
El riesgo puede ser una caja negra. La decisión no.
Basado en casos reales anonimizados, y sin material de ninguna marca ni producto.
Público objetivo: CISOs, responsables de riesgo y GRC, auditores internos y líderes de seguridad que deben defender presupuestos y decisiones ante dirección, auditoría o aseguradoras.
Duración preferida: 60 minutos, con 45 de exposición y 15 de preguntas.
Idioma de la charla: español.
Requisitos técnicos: proyector y audio estándar.
Más allá del perímetro: concientización omnicanal para terceros en es
Cuando se habla de concientización en seguridad, la mayoría de las empresas mira hacia adentro: capacitar a los empleados para que no caigan en phishing ni en ingeniería social. ¿Y los riesgos que viven afuera?
En industrias como la banca, las fintech, las cripto y los seguros, los reguladores exigen que la concientización llegue también a clientes, socios y proveedores.
En esta sesión vemos cómo diseñar campañas de concientización omnicanal que funcionen: redes sociales, alertas dentro de la app, influencers, afiches en sucursales y más. Quienes asistan verán cómo adaptar un mismo mensaje central a distintas audiencias, medir si realmente se retiene e integrar las campañas externas e internas en un único relato de seguridad.
Si el objetivo es convertir a todo el ecosistema, y no solo a los empleados, en aliados activos frente a las amenazas, esta charla ofrece el plano para hacerlo.
Público objetivo: responsables de concientización, seguridad, GRC, marketing y comunicaciones en industrias reguladas (banca, fintech, cripto, seguros).
Duración preferida: 30 a 45 minutos.
Idioma: español o inglés.
GPT-Crime: cibercrimen y ciberseguridad impulsados por IA en es
La inteligencia artificial ya no es una tendencia futura: es una fuerza presente que está cambiando tanto el cibercrimen como la ciberseguridad. Esta sesión empieza mostrando cómo los delincuentes ya usan herramientas de IA para escalar y afinar sus ataques: desde phishing automatizado y deepfakes hasta malware adaptativo y la explotación dirigida de vulnerabilidades en los propios modelos de IA. A través de ejemplos reales, se verá cómo estas herramientas transforman el panorama de amenazas y elevan la exigencia para quienes defienden.
Después, el foco pasa al otro lado: casos de uso concretos en los que la IA se está volviendo una aliada de los equipos de seguridad. Desde la detección de amenazas en tiempo real y la automatización de la respuesta a incidentes hasta la priorización inteligente del riesgo y las estrategias de resiliencia, se explora cómo las organizaciones ya la integran en sus operaciones de seguridad.
La sesión cierra con una reflexión: la IA no es buena ni mala en sí misma, su impacto depende de cómo se decida usarla. En un mundo donde la velocidad y la escala definen tanto los ataques como las defensas, una adopción ética y estratégica de la IA será clave para ir un paso adelante.
Qué se llevan los asistentes:
Entender cómo los ciberdelincuentes explotan la IA para automatizar y escalar ataques.
Conocer casos de uso reales de IA aplicada a la ciberseguridad.
Aprender estrategias prácticas para defenderse de amenazas impulsadas por IA.
Público objetivo: profesionales de seguridad, TI, riesgo y GRC, y líderes que necesitan entender el impacto de la IA en el cibercrimen y en la defensa. Nivel general.
Duración preferida: 60 minutos
Idioma: español o inglés.
Presentada y actualizada desde 2022.
Requisitos técnicos: proyector y audio estándar.
Hackers Are From Mars and Executives Are From Venus en es
Presupuestos que nunca se aprueban, incidentes donde todos buscan a quién culpar, proyectos de los que seguridad se entera solo cuando algo ya salió mal: no son fallas técnicas, son fallas de comunicación.
En esta sesión se explora la brecha cultural y de lenguaje entre los equipos de ciberseguridad y los ejecutivos: por qué piensan distinto, hablan distinto y a menudo se malinterpretan. A partir de ejemplos reales y años de experiencia en directorios, se muestra cómo decodificar el lenguaje del negocio y traducir los riesgos técnicos en prioridades estratégicas.
Quienes asistan verán cómo plantear conversaciones de ciberseguridad que resuenen con los líderes, ganar credibilidad y convertir el “no” en un “¿cuándo podemos empezar?”. Porque ganarse un lugar en la mesa no es hablar más fuerte, sino hacerse entender.
Qué se llevan los asistentes:
Decodificar cómo los ejecutivos enmarcan el riesgo y traducir los riesgos técnicos en prioridades estratégicas.
Estructurar una conversación de ciberseguridad que construya credibilidad ante la dirección.
Convertir un “no” en un “¿cuándo podemos empezar?”.
Público objetivo: líderes de ciberseguridad (CISOs, CIOs, responsables y gerentes de ciberseguridad).
Duración estimada: 45 a 60 minutos.
Idioma: español o inglés.
Requisitos técnicos: proyector y audio estándar.
Pitching cybersecurity: Traduciendo iniciativas de ciberseguridad a lenguaje de negocios en es
En el exigente entorno actual de la ciberseguridad, comunicar el valor de las iniciativas de seguridad a ejecutivos no técnicos es fundamental. Esta sesión aborda la brecha de comunicación entre los profesionales de ciberseguridad y los líderes de negocio, con estrategias prácticas para que los ejecutivos comprendan, respalden y aprueben los proyectos.
En el centro está el Security Enabler Canvas, una herramienta diseñada por mí para traducir los desafíos técnicos de ciberseguridad en conversaciones estratégicas de negocio con la alta dirección.
Quienes asistan aprenderán a:
Entender qué esperan los ejecutivos y directores cuando reciben una propuesta de ciberseguridad, y adaptar la presentación a esas expectativas.
Mapear y presentar un proyecto en lenguaje de negocio, con marcos como el Business Model Canvas.
Alinear los objetivos de ciberseguridad con los del negocio, para que el proyecto resuene con las prioridades ejecutivas.
Público objetivo: líderes de ciberseguridad (CISOs, CIOs, responsables y gerentes de ciberseguridad) y profesionales que presentan proyectos a la dirección.
Duración: 45 a 60 minutos. Existe una versión práctica de 2 horas (Learning Lab).
Idioma: español o inglés.
Presentada en: ISC2 Security Congress 2024 (4,8/5 de los asistentes), ISACA Uruguay, Ekoparty 2025.
Requisitos técnicos: proyector y audio estándar.
Series B(reach): cómo las startups pueden usar la ciberseguridad para crecer en es
Las startups prosperan con la velocidad, pero esa misma velocidad las convierte en blanco fácil. Los atacantes saben que las empresas en etapa temprana suelen estar poco defendidas, mientras que los clientes corporativos y los inversores ya esperan una due diligence de ciberseguridad rigurosa antes de firmar contratos o poner dinero.
Esta sesión está dirigida a CTOs y CISOs de startups en crecimiento. Recorre el camino desde la idea hasta la salida a bolsa y muestra cómo la madurez en seguridad tiene que evolucionar junto con el negocio. Quienes asistan verán:
Los principales riesgos cibernéticos que golpean de forma desproporcionada a las startups.
Los controles de seguridad que exigen clientes e inversores en cada etapa de financiamiento.
Cómo pasar de ver la ciberseguridad como una carga de cumplimiento a usarla como acelerador de ventas y como impulso de la valuación.
Basada en brechas reales, datos concretos y hojas de ruta pragmáticas, la charla replantea la seguridad como la diferencia entre escalar con éxito o estancarse en la “Series B(reach)”.
Público objetivo: Fundadores, CTOs y CISOs de startups en crecimiento.
Nivel: intermedio.
Duración: 45 minutos.
Idioma: español o inglés.
Requisitos técnicos: proyector y audio estándar.
The Governance Retrofit: moldear la cultura antes de que ella moldee el riesgo en es
El CEO entró y dijo: “Ahora todos usamos IA”. La sala aplaudió. Nadie hizo las preguntas difíciles.
Sin política. Sin inventario. Sin expectativas definidas. Sin una respuesta a qué significa realmente “usar IA”: qué datos pueden circular y hacia dónde, qué herramientas están aprobadas, qué pasa cuando algo sale mal. Solo un mandato. Y un vacío cultural que la organización llenó a su manera.
Así empieza la Shadow AI. No con mala intención, sino con obediencia.
La gente hizo exactamente lo que se le pidió. Usó IA, toda la que encontró: cuentas personales con datos corporativos, integraciones no autorizadas, agentes sin gobierno y con acceso irrestricto a sistemas sensibles. Optimizaron para el único objetivo claro que tenían. El informe de IBM de 2025 indica que las organizaciones con altos niveles de shadow AI pagaron en promedio USD 670.000 más por brecha que las que tenían pocos o ninguno.
Entonces llegó seguridad con controles, y seguridad pasó a ser el enemigo. No porque los controles estuvieran mal: eran necesarios. Pero llegaron después que la cultura. Cada restricción se convirtió en un obstáculo para lo que la dirección había pedido explícitamente. El equipo de seguridad no peleaba contra una amenaza: peleaba contra el mandato del propio CEO. Los empleados aprendieron a esquivarlo, porque su objetivo era claro y los controles eran solo fricción.
La mayoría de las organizaciones ya tiene este problema. Esta sesión no trata de construir gobernanza de IA desde cero, sino de incorporarla a una cultura que ya tiene sus propias reglas, y ganar igual.
El Governance Retrofit es un marco de cuatro capas para organizaciones que necesitan gobernar la cultura de IA desde donde están:
Primero el inventario. No se puede gobernar lo que no se sabe que existe. Un inventario de IA no es burocracia: es la superficie de riesgo real.
Política como comunicación, no como cumplimiento. El primer documento de gobierno tiene que hablar el idioma del negocio. Un memo legal que nadie lee no es gobierno: es teatro.
Cultura antes que controles. Los controles frenan la conducta incorrecta; la cultura instala la correcta. Aplicados en el orden equivocado, no se gobierna: se negocia contra uno mismo.
Medir lo observable. No políticas firmadas ni horas de capacitación, sino el comportamiento real: qué herramientas, qué datos, qué cuentas.
Quienes asistan se llevarán una secuencia de gobierno que pueden implementar desde el primer día, y el lenguaje para convencer a la dirección que originó el problema.
Público objetivo: CISOs, CIOs, responsables de riesgo y GRC, y líderes de gobernanza de IA.
Nivel: intermedio. Formato: keynote.
Duración: 45-60 minutos.
Idioma: español o inglés.
Requisitos técnicos: proyector y audio estándar.
ISACA North America 2027 Upcoming
2025 Secure Carolinas Conference Sessionize Event
Jorge Litvin
Founder & CEO | Safe-U
Buenos Aires, Argentina
Links
Actions
Please note that Sessionize is not responsible for the accuracy or validity of the data provided by speakers. If you suspect this profile to be fake or spam, please let us know.
Jump to top